Introduction
Certificate-based authentication removes passwords from the equation, but it introduces a new question: how do you know when a certificate is being misused? Cloned credentials, unusual enrollment spikes, and anomalous authentication patterns can go undetected for days or longer without the right monitoring in place.
CertIQ ML Anomaly Detection provides that visibility. Built into the JoinNow Platform, it applies machine learning to certificate and authentication activity, identifying behavioral patterns that fall outside the norm and alerting administrators before incidents escalate.
Key Benefits
- Instant Anomaly Alerts: Get notified the moment CertIQ ML detects a behavioral pattern that falls outside established norms.
- Reduced Investigation Time: Alerts include full context such as certificate details, device identifiers, and timestamps, so your team can act immediately.
- Proactive Threat Containment: Catch misuse patterns early enough to revoke access before a certificate-based incident escalates.
- High-Assurance Certificates: Behavioral monitoring backs up every certificate with proof it belongs where it is.
- Continuous Behavior Monitoring: CertIQ ML establishes baselines from your authentication activity and automatically flags deviations, around the clock.
How CertIQ ML Works
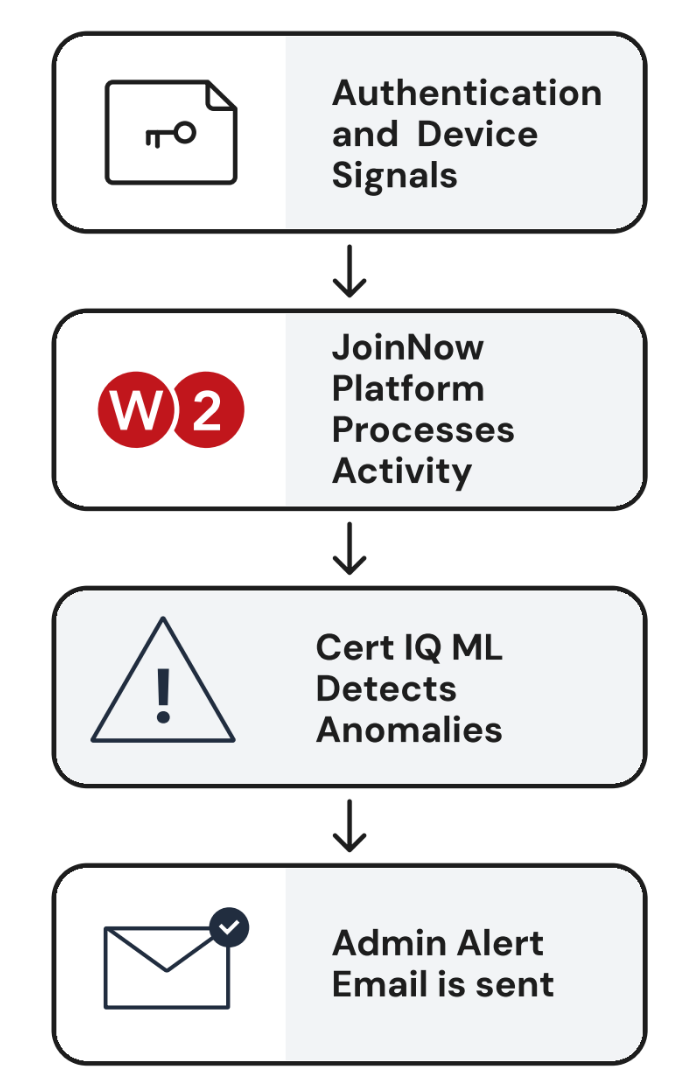
CertIQ ML continuously monitors authentication activity, device behavior, and compliance signals across your environment. Then it flags anomalies immediately.
Activity from Cloud RADIUS and connected integrations flows into CertIQ ML for analysis, surfacing anomalies that no single data point would catch on its own.
Administrators receive an instant alert with full context, such as which certificate, which devices, and when.
Catch Irregular Issuance Before Unauthorized Access Occurs
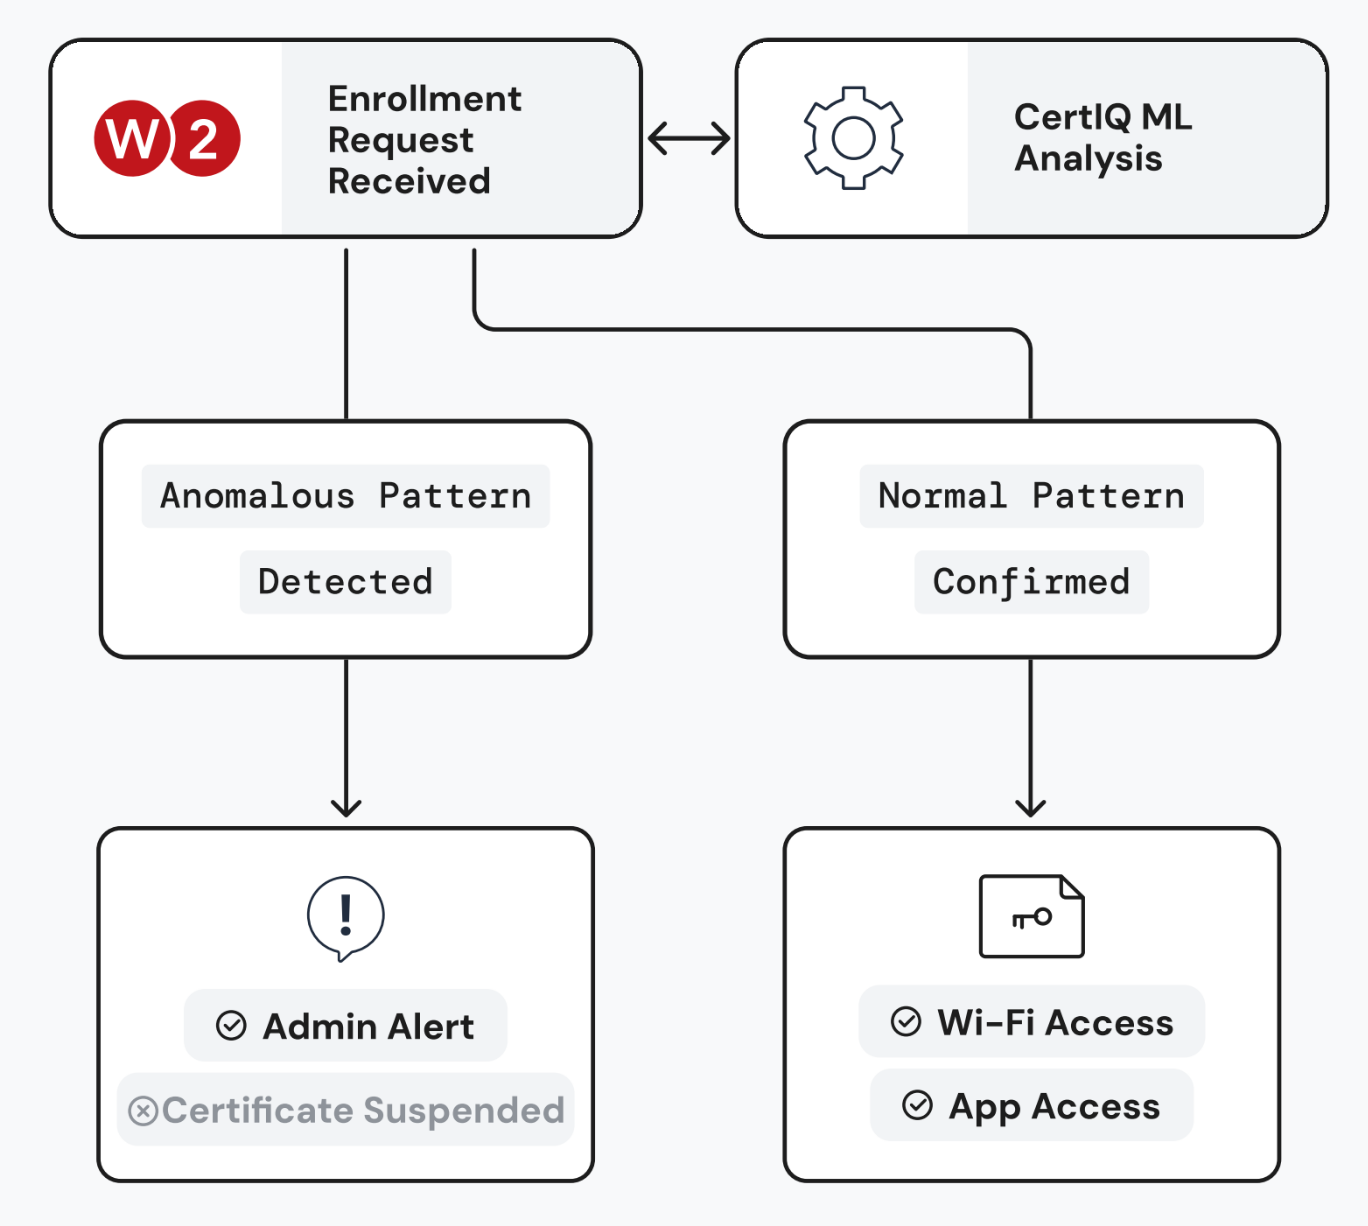
Not every threat arrives through the network. Some start at enrollment, such as a sudden spike in certificate requests, off-hours issuance attempts, or mass enrollment from unrecognized devices.
CertIQ ML monitors issuance patterns continuously and flags deviations from established baselines, giving administrators a clear signal that something is wrong before any device gains access.
Machine Learning-Driven Enrollment: CertIQ ML learns your normal issuance patterns and flags anomalies automatically, so unusual enrollment activity never goes unnoticed.
Flag Authentication Threats the Moment They Appear
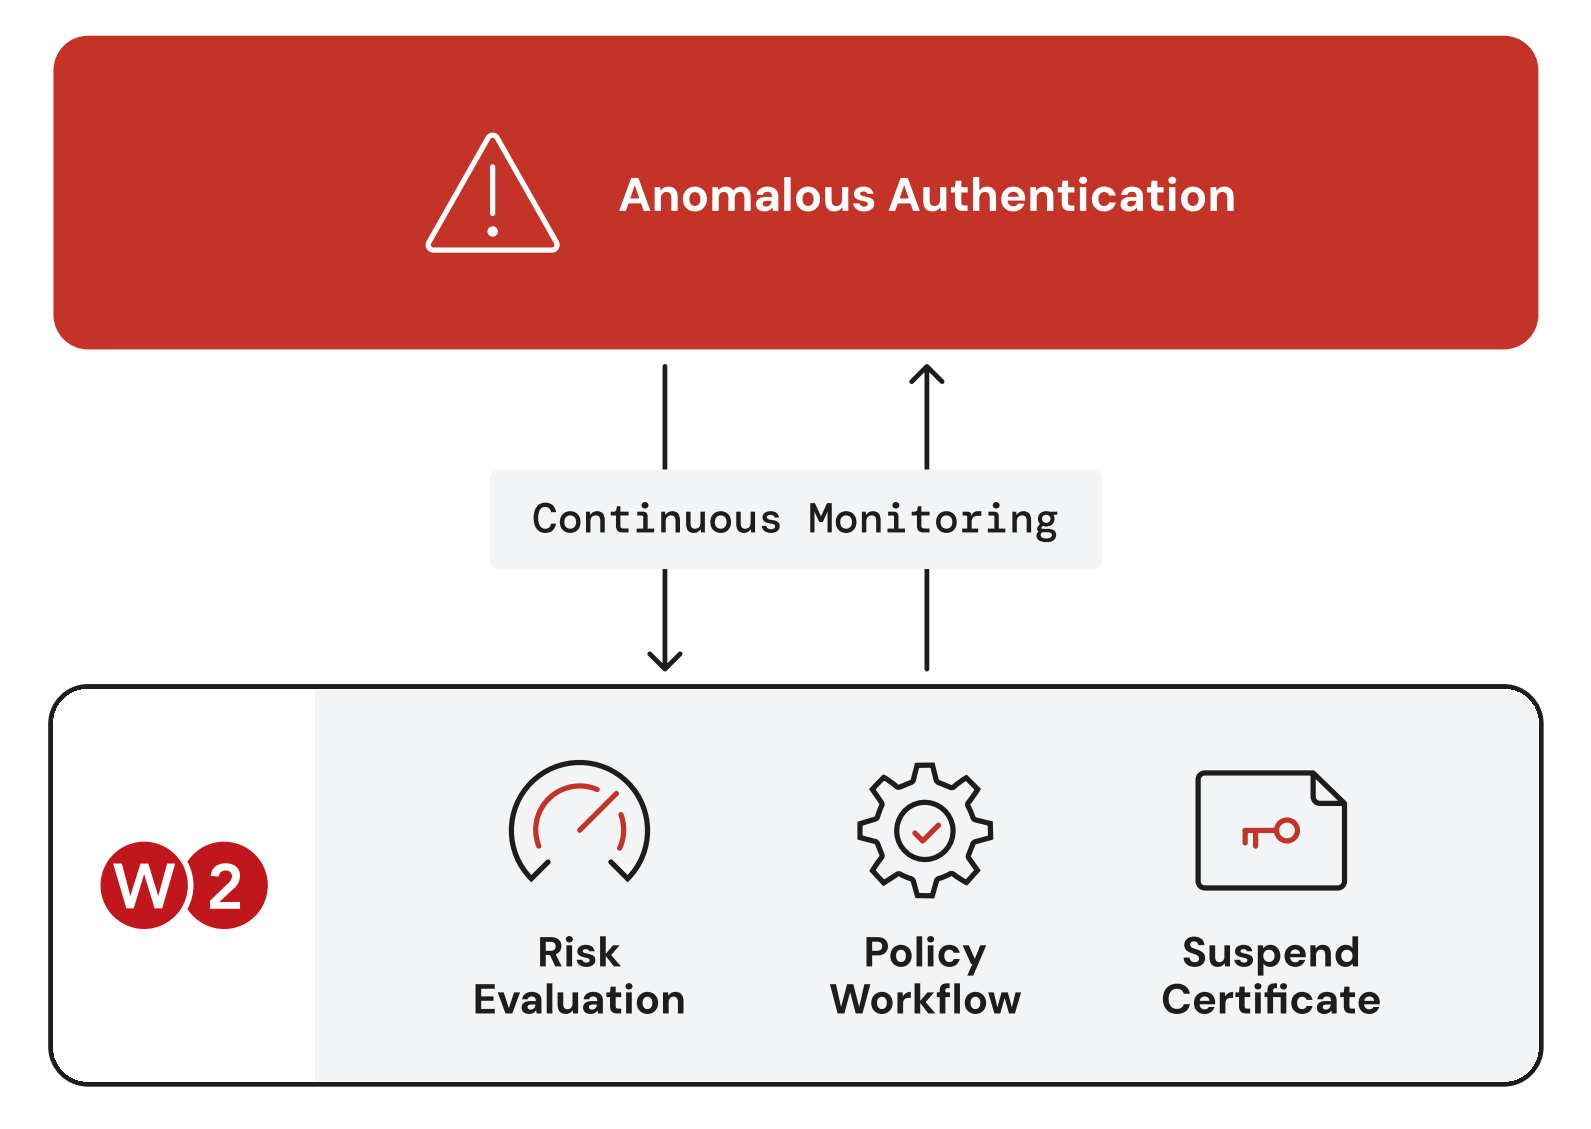
Repeated authentication attempts, unusual rejection patterns, or irregular behavior are signals worth investigating.
CertIQ ML detects anomalies across authentication patterns, network behavior, and device compliance signals, giving your team a head start before access is further exploited.
Behavioral Baseline Alerts: When authentication activity deviates from established norms, CertIQ ML flags it immediately.


