Key Takeaways
- SecureW2 won Wi-Fi Security Solution of the Year in the 2026 CyberSecurity Breakthrough Awards for its cloud PKI and phishing-resistant, certificate-based access that extends from Wi-Fi to AI agents.
- Wi-Fi passwords can be phished, shared or captured, giving attackers the same access as the user. SecureW2 replaces those passwords with device-bound certificates and verifies trust at every connection.
- The SecureW2 JoinNow Platform combines managed PKI and cloud RADIUS to automate certificate management and secure Wi-Fi access with continuous trust and without on-premises infrastructure.
A Wi-Fi password can give an attacker the same network access as the person it belongs to. Replacing shared credentials with certificate-based authentication changes how organizations verify who and what connects to their networks.
That approach earned SecureW2 the title of “Wi-Fi Security Solution of the Year” in the 2026 CyberSecurity Breakthrough Awards. Now in its 10th year, the program recognizes top companies and products across the industry and drew thousands of nominations globally.
The recognition highlights a common challenge for IT teams, which is securing the Wi-Fi networks that employees, students, contractors and guests rely on every day.
The Challenges of Securing Enterprise Wi-Fi
Securing wireless access isn’t just about getting users connected. IT teams need to authenticate employees, students, contractors and guests across a mix of devices while maintaining consistent access policies. That becomes harder when network access depends on shared credentials or authentication methods that can’t reliably establish device identity.
Yet many networks still authenticate users with passwords or legacy protocols like Protected Extensible Authentication Protocol (PEAP) with Microsoft Challenge Handshake Authentication Protocol version 2, known as PEAP-MSCHAPv2.
Those credentials can be phished, shared or captured in adversary-in-the-middle (AiTM) attacks. Once stolen, they give an attacker the same network access as the person they belong to.
Certificate-based authentication removes that weak point. A non-exportable certificate lives on the device itself, so there is no password to type, steal or reuse. Access depends on the device being known and trusted, not on what someone remembers.
Dive deeper into why Wi-Fi passwords are one of the weakest points in modern networks.
The risks associated with compromised credentials extend beyond Wi-Fi. As organizations adopt AI agents, securing the identities and credentials those agents use is becoming another part of the access security challenge.
The award highlights SecureW2 and its approach to certificate-based access, which is relevant to securing both network connections and machine identities.
Compromised credentials have been the key element in many of the most studied recent AI agent hacks. AI agents can quickly find loose credentials and hack into organizations still using pre-shared keys. We make enterprise public key infrastructure easy for teams to roll out, then we keep checking that every device on the network still deserves to be there. This recognition reflects the work our team and customers have put into making that the standard.
Bert Kashyap, CEO and Co-Founder of SecureW2
About the CyberSecurity Breakthrough Awards
The CyberSecurity Breakthrough Awards program recognizes the innovators, leaders and companies across information security.
SecureW2 Public Key Infrastructure (PKI) won the Solution of the Year award after an independent panel of expert judges evaluated the platform for its innovation, performance, ease of use, functionality, value and impact.
The 2026 awards program marks its 10th year. See the full list of 2026 winners here.
What the SecureW2 Platform Does
Securing network access starts with establishing trusted identities. SecureW2 is a leader in cloud-native PKI and RADIUS passwordless authentication, securing human, machine and AI agent identities with continuous trust.
The SecureW2 platform pairs managed JoinNow Dynamic PKI with JoinNow Cloud RADIUS for certificate-based Wi-Fi authentication without on-premises servers. It works with the identity and access management (IAM), mobile device management (MDM) and security tools teams already use, including Microsoft Entra ID, Okta, Intune and CrowdStrike.
- Phishing-resistant access: Hardware-bound certificates replace Wi-Fi passwords, so stolen credentials no longer open the network.
- Continuous trust enforcement: Device identity and compliance signals are evaluated continuously, not just at the moment of connection. If a device falls out of compliance, access can be restricted or revoked right away.
- Less infrastructure to run: Cloud RADIUS runs at up to 99.999% availability, with no RADIUS or Network Policy Server (NPS) servers to patch, size or maintain.
- Automated certificate lifecycle: Enrollment, renewal and revocation run automatically through modern protocols like Automated Certificate Management Environment (ACME) and Dynamic Simple Certificate Enrollment Protocol (SCEP).
Industry Recognition Backed by Customer Feedback
While awards recognize a solution’s strengths from an industry perspective, customer reviews reveal what those strengths mean in practice.
For IT teams evaluating Wi-Fi authentication and certificate management platforms, deployment, ongoing administration and support are important considerations.
SecureW2 earned 15 badges in the Fall 2026 G2 reports, spanning Network Access Control (NAC), SSL & TLS Certificate Tools, Certificate Lifecycle Management (CLM) and Zero Trust Networking for the mid-market. G2 customer feedback also highlights automation, ease of management and support as recurring themes in users’ experiences with SecureW2.
For example, a verified user in Education Management describes SecureW2 JoinNow in a G2 review as having “effortless onboarding, smooth integration, and stellar support.”
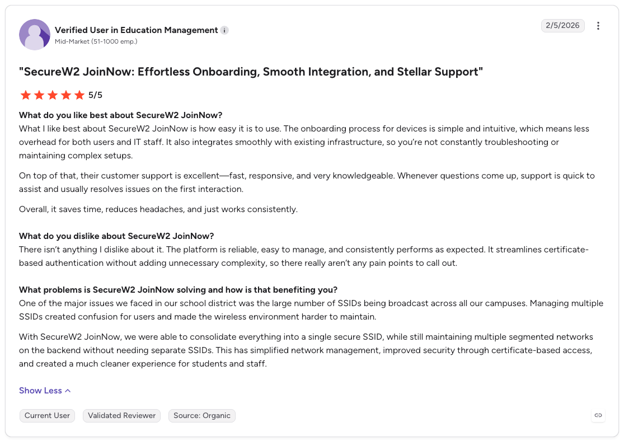
The review offers a practical perspective on what matters beyond the technology itself: making certificate-based authentication easier to deploy and manage.
For the most recent customer feedback on our PKI, Cloud RADIUS and AI agent security platform, you can browse SecureW2 reviews on G2.
Modernizing Wi-Fi Security
Certificate-based authentication provides IT teams with a reliable way to establish device identity, enforce access policies and manage authentication across their environments.
SecureW2 brings managed PKI and Cloud RADIUS together to help organizations implement certificate-based Wi-Fi authentication and maintain trust across connected devices.
If you would like to see how certificate-based Wi-Fi works with the identity and device management tools you already run, schedule a demo.
Frequently Asked Questions
What award did SecureW2 win in 2026?
SecureW2 was named Wi-Fi Security Solution of the Year in the 2026 CyberSecurity Breakthrough Awards. The program, now in its 10th year, drew thousands of nominations from around the world.
Why are Wi-Fi passwords a security risk?
Wi-Fi passwords can be phished, shared or captured in adversary-in-the-middle attacks. A stolen password gives an attacker the same network access as the person it belongs to.
How does certificate-based Wi-Fi authentication work?
A non-exportable certificate lives on the device itself, so there is no password to type, steal or reuse. Access depends on the device being known and trusted, and the SecureW2 platform verifies that trust every time a device connects.
Do you need on-premises RADIUS servers for certificate-based Wi-Fi?
Not with the SecureW2 platform. It pairs a cloud-native PKI with Cloud RADIUS, so there are no RADIUS or NPS servers to patch, size or maintain.
