Key Takeaways
- Man-in-the-middle attacks let attackers secretly intercept communications by impersonating trusted networks, websites, or devices to steal credentials, monitor traffic, or modify data without the victim knowing.
- MITM attacks are common and often target Wi-Fi networks, using techniques such as evil twin attacks, ARP spoofing, DNS spoofing, SSL stripping and browser-based attacks to steal sensitive information.
- Certificate-based authentication with EAP-TLS is the most effective defense because it uses digital certificates instead of passwords, preventing credential theft and significantly reducing the risk of MITM attacks.
If you’ve ever watched this scene from SpongeBob SquarePants, you’ve already seen the basic idea behind a man-in-the-middle (MITM) attack: two parties believe they’re communicating directly, while an attacker secretly intercepts the conversation.
While the cartoon plays it for laughs, real MITM attacks can have serious consequences. Whether they’re targeting users on public Wi-Fi, intercepting web sessions or stealing login credentials, MITM attacks exploit trust to gain access to sensitive information.
Understanding how these attacks work is key to preventing them.
What Is a Man-in-the-Middle (MITM) Attack?
A man-in-the-middle attack is a cyberattack where the attacker secretly inserts themselves between two parties that believe they’re communicating directly with one another.
Instead of information flowing straight from the sender to the recipient, it first passes through the attacker, who can monitor, steal or even modify the data before forwarding it along.
MITM attacks are difficult to detect because the connection often appears legitimate. They can target web browsing, email, mobile apps, public Wi-Fi networks and virtually any other form of network communication.
How Does a Man-in-the-Middle Attack Work?
An MITM attack begins when an attacker positions themselves between a victim and a trusted destination, such as a website, email server or Wi-Fi network. This is often done by impersonating one of the communicating parties or tricking the victim into connecting through the attacker’s infrastructure.
Once traffic is flowing through the attacker, they can monitor, capture or manipulate the data without interrupting the connection. The diagram below shows how a MITM attacker secretly intercepts communication between a victim and a trusted destination.
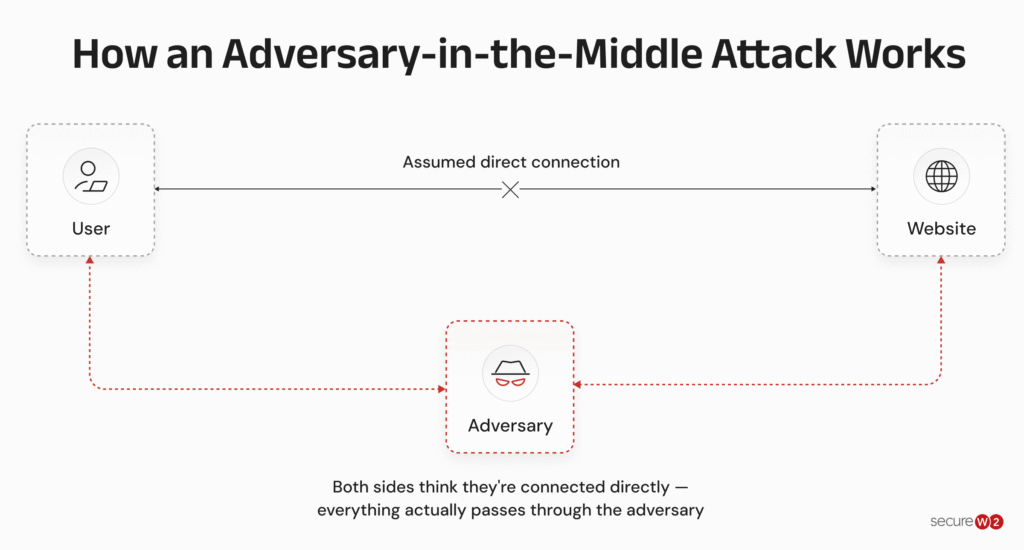
Depending on the type of MITM attack, they may steal login credentials, session cookies, financial information or other sensitive data.
Attackers use several techniques to accomplish this, from rogue Wi-Fi networks and DNS spoofing to HTTPS interception and session hijacking. While these attacks are commonly associated with unsecured networks, they can also succeed on seemingly secure connections if the users are tricked into trusting a malicious connection.
See your security gap before attackers do.
See continuous trust in action on a platform that includes RADIUS, PKI and AI security.
What Are the Phases of Man-in-the-Middle Attacks?
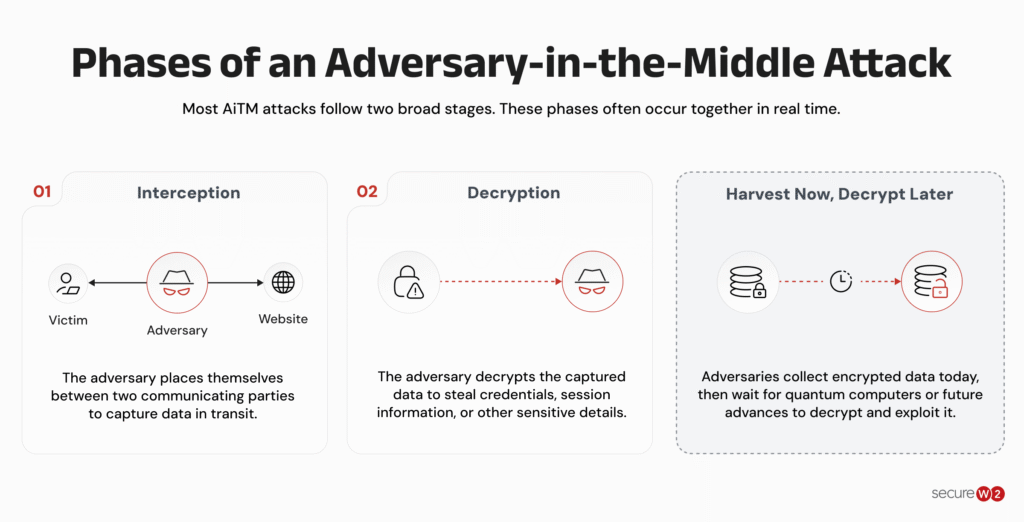
Most MITM attacks follow two broad stages:
- Interception: During this stage, the attacker gathers data by placing themselves between two communicating parties.
- Decryption: In this stage, the attacker decrypts the intercepted information.
These phases often occur together in real time, but they can occur independently.
A growing attack strategy is harvest now, decrypt later (HNDL).
In HNDL, attackers capture and store large volumes of encrypted data today without trying to decrypt it immediately. Instead, they wait until quantum computers (or other future cryptanalytic advances) become powerful enough to break current encryption algorithms (such as RSA or ECC).
Once attackers can decrypt the data, they can access and exploit the stored credentials, session data and other sensitive information.
The image below shows the two phases of a MITM attack with Harvest Now, Decrypt Later (HNDL) as a related long-term attack strategy rather than a distinct phase.
Man-in-the-Middle Attack Techniques
Attackers use several techniques to place themselves in the middle of communications that unsuspecting users believe are secure. These techniques can involve manipulating network protocols, redirecting traffic, or weakening secure connections.
ARP Spoofing (ARP Poisoning)
In Address Resolution Protocol (ARP) spoofing, attackers send forged ARP messages over a local network to associate their Media Access Control (MAC) address with the IP address of a legitimate device. This allows them to intercept, inspect or modify traffic intended for that device.
You may hear the terms ARP poisoning or ARP cache poisoning thrown around, but they don’t mean the same thing as ARP spoofing. ARP poisoning refers to any manipulation of the ARP table, while ARP spoofing is one technique used to achieve it.
DNS Spoofing
In Domain Name System (DNS) spoofing, attackers provide false DNS responses that redirect users from legitimate websites to malicious ones designed to mimic the real site. Victims unknowingly enter credentials or download malware while believing they are interacting with a trusted service.
DNS spoofing is sometimes called DNS poisoning or DNS cache poisoning. DNS poisoning, however, is a broader term for attacks that manipulate DNS information. DNS cache poisoning refers more specifically to attacks that corrupt cached DNS records.
IP Spoofing
In IP spoofing, attackers forge the source IP address of data packets to impersonate a trusted device. This can trick systems into accepting malicious traffic or sending sensitive information to the attacker.
HTTPS Spoofing
Because HTTPS can prevent spoofing, hackers have created an attack where they register domain names that mimic popular sites and send links to victims, exploiting a vulnerability in the address bar. The victim will then connect to the rogue website and become exposed to credential theft.
SSL Stripping
HTTPS is a strong security measure that has helped stop MITM attacks. Like HTTPS spoofing, this led to a new attack that involves infiltrating an online exchange, intercepting a secure HTTPS connection between a server and a web browser, downgrading HTTPS to HTTP, and connecting to the other party.
Now the hacker has complete control over the connection and can harvest the data.
Types of Man-in-the-Middle Attacks
MITM attacks can take different forms depending on what attackers target and how they intercept communications.
Email Hijacking
Email hijacking can use man-in-the-middle techniques to intercept or gain unauthorized access to email communications. Attackers may compromise a legitimate email account or spoof a trusted email address to send fraudulent messages that trick recipients into revealing credentials, wiring money, or sharing sensitive information.
Wi-Fi Eavesdropping
In Wi-Fi eavesdropping, attackers create a public Wi-Fi network with a boosted signal that closely mimics nearby networks (such as a library’s guest network). Once victims connect, attackers can monitor activity or steal login credentials.
Evil Twin Attack
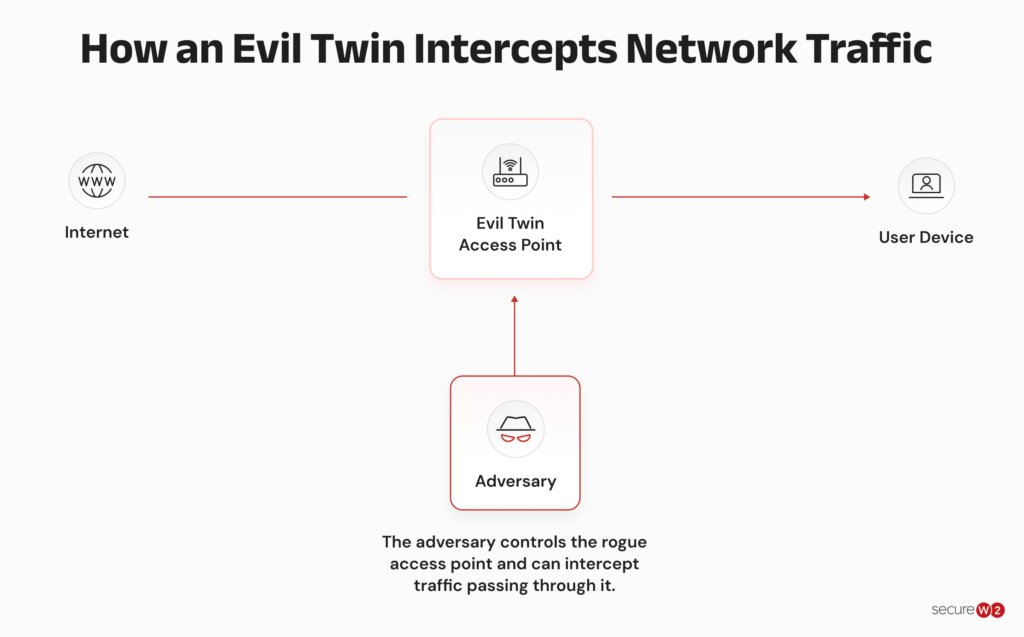
In an evil twin attack, the attacker sets up a rogue access point near the target network, usually in busy places with open Wi-Fi, like a coffee shop. The rogue access point is deployed, and the SSID (Wi-Fi name) is “spoofed”, meaning the attacker broadcasts the same name as, or a name nearly identical to, the legitimate SSID.
Anyone who connects to the false network may have their private information harvested, including passwords, usernames and other private information.
Man-in-the-Browser (MITB) Attack
A man-in-the-browser (MITB) attack occurs after malware infects a user’s browser.
Rather than intercepting traffic over the network, the malware manipulates browser sessions directly, allowing attackers to steal credentials, alter transactions or capture sensitive information even when HTTPS encryption is in use.
Real-World Examples of MITM Attacks
MITM attacks have been used in real-world incidents to intercept communications, steal credentials, and gain unauthorized access to systems and devices. Here are some notable examples:
- Tesla Phone Key Attack (2024): Researchers demonstrated a MITM phishing attack using a spoofed Wi-Fi network at a Tesla charging station. Stolen credentials and an OTP enabled the attacker to add a new phone key and unlock the vehicle.
- Secret Blizzard AiTM Campaign (2025): Microsoft reported Secret Blizzard targeting foreign embassies in Moscow with an adversary-in-the-middle (AiTM) position at the ISP/telco level. Microsoft reported the AiTM position allowed TLS/SSL stripping that exposed most browsing traffic in clear text, including certain tokens and credentials.
- Forest Blizzard DNS Hijacking and AiTM (2026): Microsoft reported Forest Blizzard compromising SOHO routers to hijack DNS requests and support targeted AiTM attacks against TLS connections. In some cases, attackers redirected victims to their infrastructure to intercept traffic, including communications with Outlook on the web.
What Makes Man-in-the-Middle Attacks So Dangerous?
MITM attacks can cause so much damage because they allow attackers to slip into a network undetected, steal private data and leave before anyone suspects anything.
Even if the attack is discovered and stopped, attackers often retain any credentials or data they have already captured.
The consequences of cyberattacks are costly. According to IBM’s Cost of a Data Breach Report, the global average cost of a data breach was $4.99 million in 2026.
Beyond a financial impact, businesses affected by a successful MITM attack can lose customer trust, face operational disruption and spend significant time and resources recovering from the incident.
How Common Are Man-in-the-Middle Attacks?
Man-in-the-middle attacks are incredibly common primarily because Wi-Fi is an easy attack vector.
MITM often exploits something people do every day: connect to trusted Wi-Fi networks. Many devices automatically attempt to reconnect to previously saved network names, giving attackers an opportunity to create rogue access points, such as evil twin networks, that impersonate legitimate Wi-Fi.
If your laptop or your phone sees the name of a Wi-Fi network that you’ve connected to before and it’s a strong signal, it’s just going to start trying to connect to it. When it tries to connect to it, it’s going to send its credentials over, no matter who’s actually broadcasting the Wi-Fi signal. When hackers do this, it’s called an adversary-in-the-middle or evil twin attack. They can use this to harvest credentials to decrypt later, or ‘pass-the-hash’ as some network infrastructure will just accept the hashed credentials.Micah Spady, Director of Product Marketing at SecureW2
How to Detect a MITM Attack
As MITM attacks become more advanced, detecting them can be challenging. Here are a few signs to watch out for:
- Suspicious URLs: MITM attacks may involve fake websites built to look exactly like a website you know and trust. They may use URLs very close to the real web page, with only a small change, such as a 0 instead of an o. Thoroughly examine the web address and the page itself to ensure it’s legitimate before entering any credentials.
- High latency: Although uncommon, unexpected latency spikes combined with other suspicious behavior may indicate traffic interception.
- Frequent disconnections: Repeatedly being logged out of apps or websites and having to re-enter your credentials can be a sign of an MITM attack.
- Unsecured website browser notifications: Don’t ignore warnings from your browser that a website may not be secure.
If any of these things are happening, there are steps you can take to force the MITM to stop.
Can You Stop a MITM Attack?
It’s difficult to catch a MITM attack in real time, which is why they’re so dangerous.
However, if you happen to notice one is happening, the best measures to keep the attacker from getting any more information are:
- Disabling your Wi-Fi connection
- Switching your connection to a secure VPN, if applicable
- Removing the root or intermediate certificate authority (CA) from the network, if applicable
- Running a malware detection program on your device and taking necessary steps to remove any malware detected
The best way to stop a MITM attack is to prevent it from occurring in the first place.
How to Prevent Man-in-the-Middle Attacks
There are several ways you can protect your network and prevent man-in-the-middle attacks. These include:
- Enabling 802.1X authentication
- Using a Wireless Intrusion Prevention System (WIPS)
- Replacing credentials with digital certificates
The most secure method is to configure your devices with certificates and authenticate with EAP-TLS.
Certificates serve as unique identifiers and can be bound to devices and servers for easy identification. The associated private keys remain securely stored on the device, enabling strong mutual authentication without transmitting passwords.
The security plan that scales with you.
Our solutions can scale from mid-market to global enterprises. Compare options and see how our solutions protect you from costly breaches and ensure peace of mind.
AI-Assisted MITM Attacks
Man-in-the-middle attacks have always relied on a relatively simple formula: position an attacker between two communicating parties, intercept the traffic or credentials being exchanged, and avoid detection long enough to exploit the collected information.
Security agencies warn that advances in artificial intelligence are making all three of these steps easier and faster than ever.
In June 2026, the cybersecurity agencies of the Five Eyes alliance (CISA and NSA in the United States, the UK’s National Cyber Security Centre (NCSC), the Canadian Centre for Cyber Security, the Australian Signals Directorate, and New Zealand’s National Cyber Security Centre) issued a joint statement warning that advanced AI models are expected to fundamentally change both offensive and defensive cyber operations within months, not years.
The advisory specifically highlights how AI is lowering the barrier to entry for cyber attackers while increasing the speed, scale and sophistication of attacks.
For MITM attacks, this warning has direct implications. AI-assisted tools can automate tasks that previously required significant expertise and manual effort. This includes:
- Generating convincing phishing campaigns
- Creating realistic fake login portals
- Deploying rogue wireless access points
- Analyzing captured credentials or session data at scale
What once required a skilled attacker with specialized knowledge can increasingly be accomplished using automated tooling and AI-assisted workflows.
The risk is particularly significant in wireless environments. Traditional evil twin and rogue access point attacks have historically required attackers to understand wireless configurations, authentication methods, and credential-capture techniques.
AI-assisted attacks can automate a lot of this process by dynamically adapting to observed network configurations, creating convincing enterprise wireless profiles, and processing captured credentials with minimal human intervention.
This evolving threat reinforces why certificate-based authentication has become increasingly important for enterprise wireless security. Even a highly convincing rogue access point broadcasting the correct SSID cannot successfully impersonate the legitimate network without possessing a valid server certificate trusted by the client, when clients are configured to validate the RADIUS server certificate.
As AI continues to lower the technical barriers to launching sophisticated attacks, authentication methods that eliminate opportunities for credential theft altogether are becoming less a security best practice and more a security requirement.
Defending Against MITM Attacks With Certificate-Based EAP-TLS Authentication
While EAP-TLS, EAP-TTLS/PAP, and PEAP-MSCHAPv2 all use TLS, only EAP-TLS authenticates users and devices exclusively with digital certificates rather than passwords.
Many major companies are switching to certificate-based authentication because EAP-TLS offers superior network security. With EAP-TLS, you mitigate the risk of MITM attacks because you’re not sending credentials over the air.
EAP-TLS requires certificates, and organizational onboarding software can configure all devices for network authentication correctly. This automated enrollment eliminates manual configuration and prevents devices from sending credentials to a rogue actor.
The video below shares how MITM attacks exploit weaknesses in improperly configured 802.1X networks.
Simplify EAP-TLS Deployment With SecureW2
Deploying EAP-TLS across an organization requires more than issuing certificates. IT teams also need to manage certificate enrollment, renewal and revocation, configure devices correctly, and maintain the infrastructure that supports authentication.
The SecureW2 JoinNow platform simplifies certificate enrollment for managed and unmanaged devices through methods such as ACME Device Attestation (ACME DA), Dynamic SCEP and SAML-based authentication.
With JoinNow Cloud RADIUS and real-time policy enforcement, SecureW2 helps organizations deploy and manage certificate-based authentication across major operating systems and device environments.
Schedule a demo to see how SecureW2 can simplify your EAP-TLS deployment.
Frequently Asked Questions
Do VPNs protect from man-in-the-middle attacks?
Virtual private networks (VPNs) encrypt internet traffic between a device and a VPN server, helping protect data from interception. However, VPNs can still be vulnerable to attacks, particularly when authentication relies on passwords that attackers can steal or exploit. Certificate-based authentication can provide stronger protection against credential theft.
Can TLS be hacked?
TLS itself is a robust encryption protocol, but its effectiveness depends on proper implementation. Password-based methods like EAP-TTLS/PAP or PEAP-MSCHAPv2 leave networks highly vulnerable to MITM attacks because attackers can intercept or trick credentials during authentication.
Can firewalls stop man-in-the-middle attacks?
Firewalls are necessary for network security and can block many unauthorized access attempts, but they are generally ineffective against MITM attacks on their own. MITM exploits often occur by impersonating legitimate traffic or exploiting Wi-Fi weaknesses (such as evil twin attacks), which can bypass traditional firewall rules.
Can a man-in-the-middle attack happen on a secure HTTPS website?
Yes, though it’s harder. Attackers use techniques like SSL stripping (downgrading to HTTP), fake certificates or exploiting browser misconfigurations. Proper certificate validation and EAP-TLS on the network level provide stronger protection.
How do digital certificates prevent MITM attacks?
Certificates act as unique, cryptographically signed digital IDs for users, devices and servers. With EAP-TLS, devices authenticate mutually without sending passwords over the air, blocking impersonation attempts common in MITM attacks.
Are man-in-the-middle attacks common?
Man-in-the-middle attacks are a common cybersecurity threat, particularly on unsecured networks and through phishing. Using HTTPS, strong authentication, certificate validation, and secure Wi-Fi can reduce the risk of MITM attacks.
How do you remove a man-in-the-middle attack?
To remove a MITM attack, disconnect from the compromised network, change affected passwords, revoke compromised sessions or credentials, and remove unauthorized certificates or devices. Then reconnect through a trusted, secure network.
