We’re excited to announce our latest release, 8.6. Here’s a quick overview of what’s new across the JoinNow platform.
- Device security signals for Generic OAuth: Validate device posture before enrollment or authentication.
- Email Address Lookup for Okta: Choose an email address or username for Okta user lookups.
- Single-Command Wired 802.1X for Linux: Enroll TPM-backed certificates and connect with a single command.
- Reliable Certificate Downloads for ECDSA and ML-DSA: Reliable downloads for all signature algorithms.
Device Security Signals for Generic OAuth
In this update, Generic OAuth signal sources tap into your MDM data to complete device posture checks. Noncompliant devices are stopped during initial enrollment, before a certificate is issued. Because posture checks run at every RADIUS re-authentication, any device that drops out of compliance is promptly disconnected when it re-authenticates, rather than staying connected until its certificate expires. This capability supports any platform or MDM that provides an OAuth-secured API, including Workspace ONE, Google Workspace, and Jamf Pro.
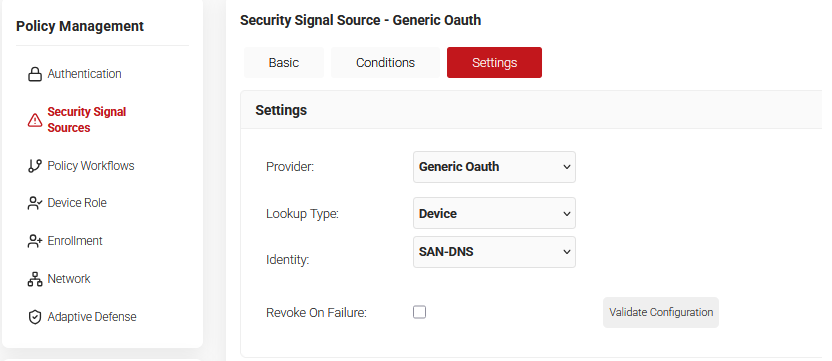
To configure, navigate to Security Signal Sources → create a new API → choose Device as the lookup type.
Email Address Lookup for Okta
Historically, Okta user lookups relied only on usernames. With this release, administrators can choose to look users up by email address instead. This supports organizations that don’t use Okta usernames to identify users. Each configuration uses a single lookup method. Username remains the default, so existing configurations are unaffected.
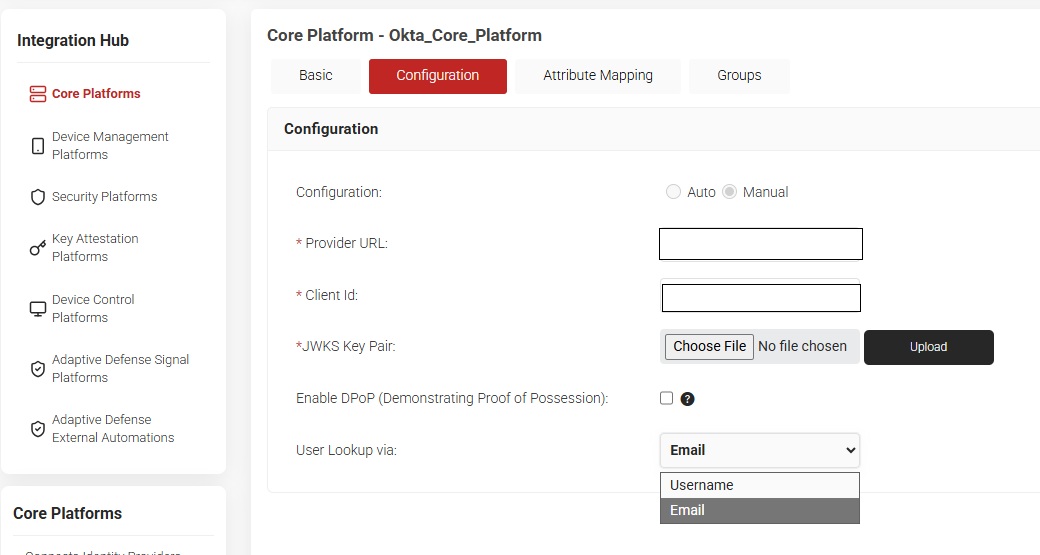
To configure, go to your Core Provider settings → Configuration → select your preferred lookup option from the User Lookup drop-down.
Single-Command Wired 802.1X for Linux
Getting Linux devices onto wired 802.1X has meant handling certificate enrollment and network setup as separate tasks. In 8.6, a single command does both. A Linux device enrolls for a TPM-backed certificate and connects to the wired network in one step, and the private key never leaves the TPM.
Reliable Certificate Downloads for ECDSA and ML-DSA
Select certificate downloads using ECDSA or ML-DSA signature algorithms were failing intermittently with signature errors. This is now fixed, and certificates download reliably across signature algorithms.
We are dedicated to ongoing platform enhancements and maintaining our leadership in industry standards. By choosing SecureW2, your environment benefits from these continuous advancements with every update.
To discover how we can deliver passwordless security to your organization, speak with one of our experts. Existing SecureW2 customers can access detailed release documentation directly within the JoinNow portal or contact their dedicated customer success manager for further details.
