How to Setup EAP-TLS with Workspace One

Introduction

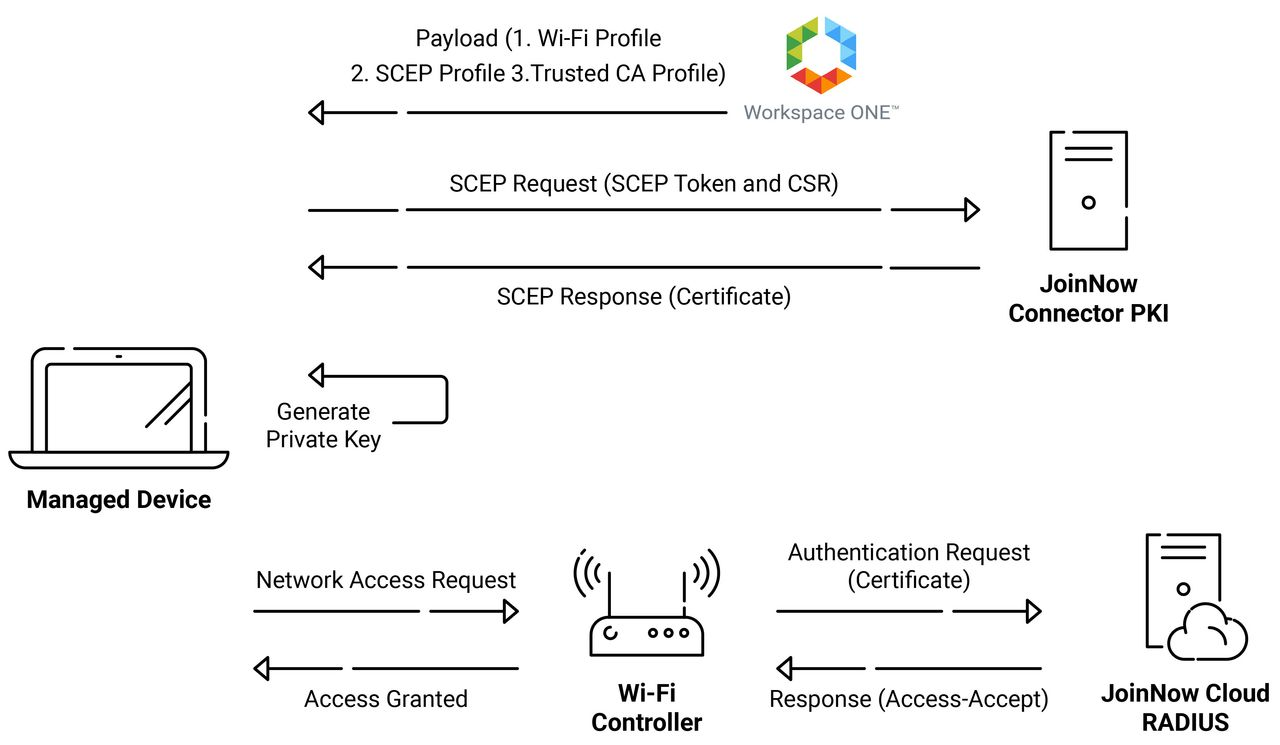
The Simple Certificate Enrollment Protocol (SCEP) is a protocol commonly used with Mobile Device Management (MDM) systems to automate the certificate life cycle for their managed devices. The Simple Certificate Enrollment Protocol uses a combination of a unique API URL and a Shared Secret, distributed to devices in a SCEP Profile, that enables the devices to enroll themselves for certificates without any user intervention. The SCEP enrollment helps IT Admins save some time compared to enrolling certificates for the MDM manually.

This enables devices to be configured for certificate-based Wi-Fi authentication from the Certificate Authority (CA) of your choosing the instant they open their laptop. Using an SCEP profile to enable certificate-based authentication allows business users to improve their network security by safeguarding their devices from insecure password-based authentication.

See your security gap before attackers do.

See continuous trust in action on a platform that includes RADIUS, PKI and AI security.

Customize Your Video Demo

Workspace ONE is a type of digital platform that provides services for IT admins to operate Mobile Device Management (MDM) and Mobile Access Management (MAM) from the Cloud Management. For certificate enrollment in the SCEP protocol, the MDM, such as Workspace ONE, offers SCEP that devices can use to request certificates from our Public Key Infrastructure (PKI). In this document, you will see the configuration of Extensible Authentication Protocol-Transport Layer Security (EAP-TLS) with Workspace ONE.

Prerequisites

The following are the prerequisites for configuring the SCEP profile using our Public Key Infrastructure (PKI) with Workspace ONE Powered by AirWatch:

  1. End users can enroll their devices with Workspace ONE.
  2. A certificate for Apple push notifications has been created and uploaded to Workspace ONE.

Configuring JoinNow Management Portal

This section describes how to configure the JoinNow Management Portal to issue certificates to Workspace ONE-managed devices through the SecureW2 SCEP Gateway integration.

  1. Creating an Intermediate CA for Workspace ONE SCEP Gateway Integration
  2. Creating a Device Management Platform
  3. Configuring the Default Workspace ONE Certificate Template
  4. Configuring the policies (Policy Workflow and Enrollment Policy)

Creating an Intermediate CA for Workspace ONE SCEP Gateway Integration

In this section, you’ll create an intermediate CA that issues certificates to Workspace ONE-managed devices.

SecureW2 recommends using a new intermediate CA for this integration. The CA that issues certificates for BYOD devices should be separate from the CA that issues certificates for managed devices, because managed devices do not require email notifications. With a dedicated CA, you can disable email notifications for Workspace ONE-managed devices.

To create a new intermediate CA, perform the following steps:

  1. Log in to the JoinNow Management Portal.
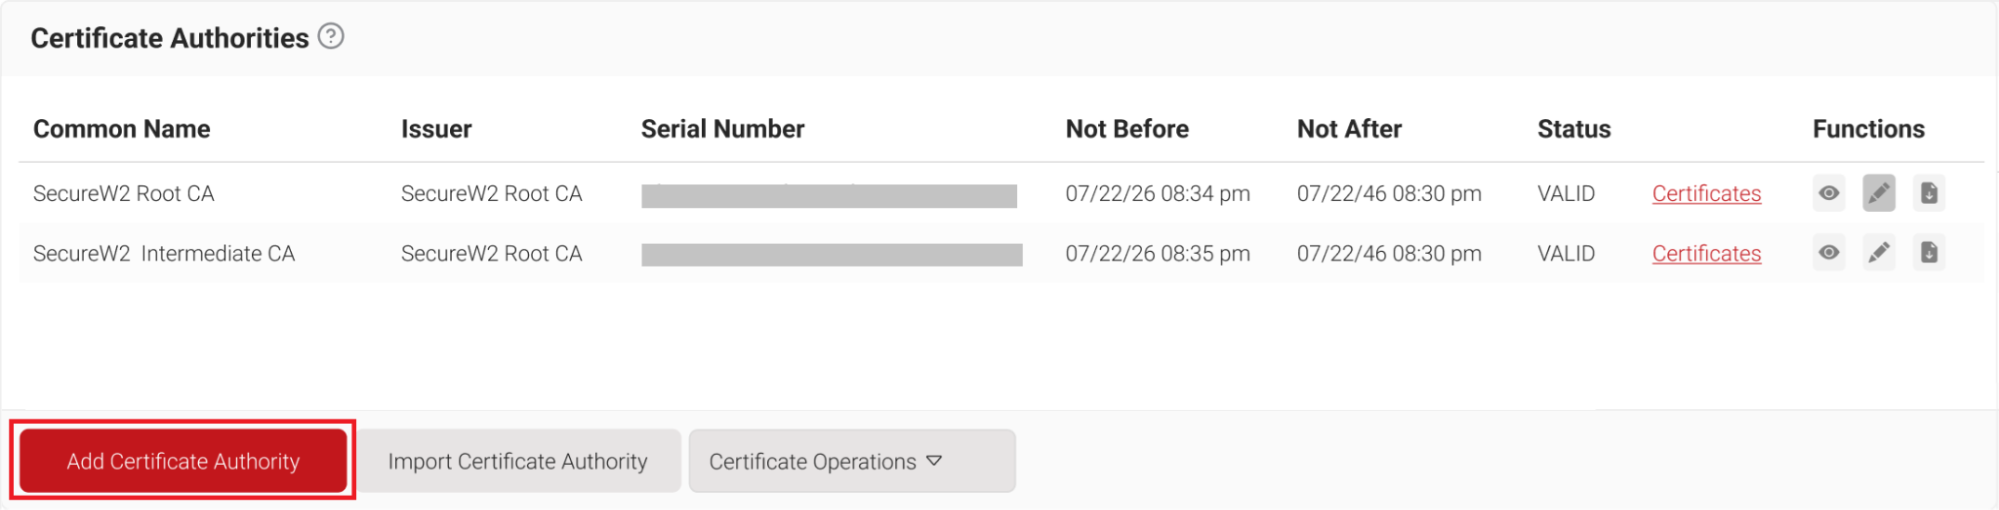
  2. Navigate to Dynamic PKI > Certificate Authorities.
  3. Click Add Certificate Authority.
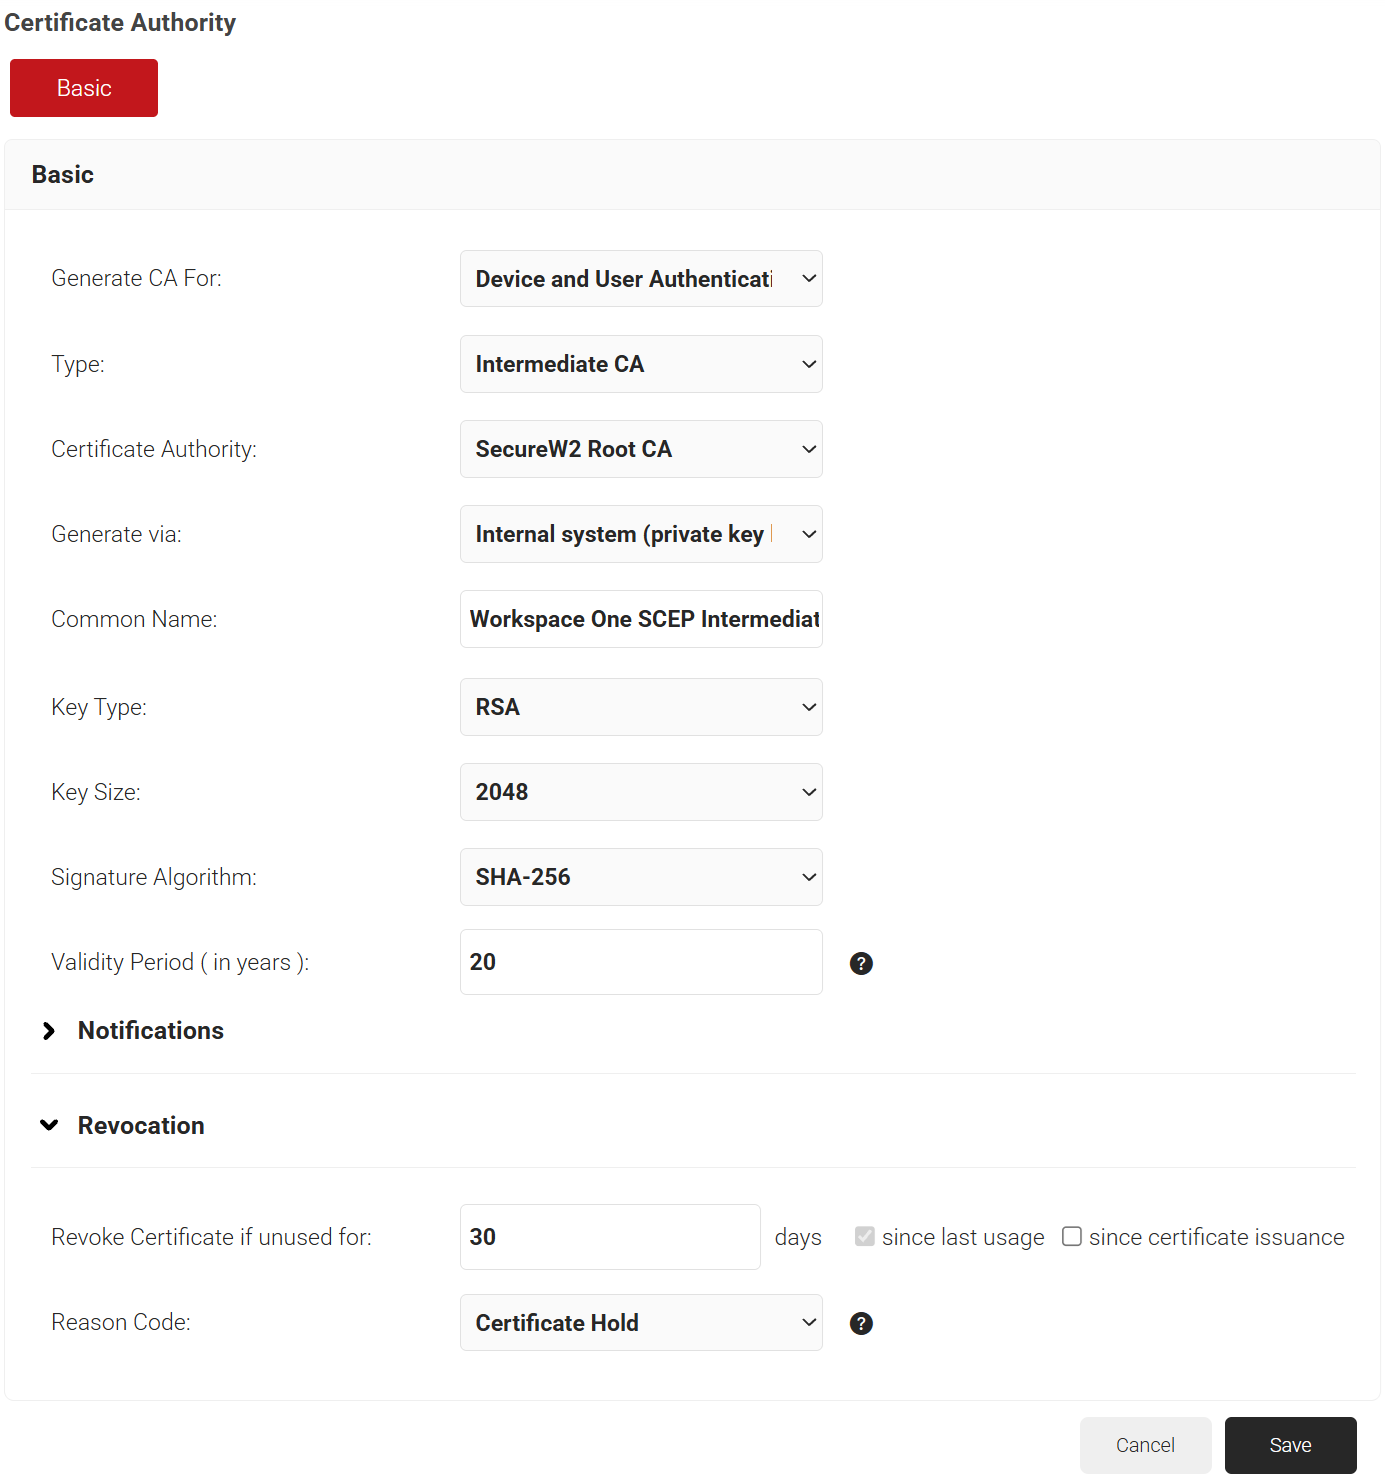
  4. In the Basic section, from the Generate CA For drop-down list, select Device and User Authentication to authenticate devices and users.
  5. From the Type drop-down list, select Intermediate CA.
  6. From the Certificate Authority drop-down list, select the default Root CA that comes with your organization.
  7. In the Common Name field, enter a common name for the CA certificate. SecureW2 recommends a name that includes “SCEP.”
  8. From the Key Size drop-down list, select 2048 for the CA certificate key pair.
  9. From the Signature Algorithm drop-down list, select the signature algorithm for the certificate signing request. The option available is SHA-256.
  10. In the Validity Period (in years) field, enter the validity period of the CA certificate.
  11. In the Notifications section:
    1. From the Expiry Notification Frequency (in days) drop-down list, select the frequency interval for which a certificate expiration notification should be sent to users.
    2. Select the Notify user on successful Enrollment check box to notify users after a successful enrollment.
  12. In the Revocation section:
    1. In the Revoke Certificate if unused for field, select the number of days after which an unused certificate can be revoked.
      1. Since last usage – Select this checkbox to revoke the certificate after a specified number of days if it remains unused.
      2. Since certificate issuance – Select this checkbox to revoke the certificate after a specified number of days after it is issued.
    2. From the Reason Code drop-down list, select any one of the following reasons for which the certificate is revoked.
      1. Certificate Hold
      2. AA Compromise
      3. Privilege Withdrawn
      4. Unspecified
  13. Click Save. The new intermediate CA is generated.

Creating a Device Management Platform

The device management platform provides the Enrollment URL and the API Secret. You enter these in the Certificate Authority settings in Workspace ONE UEM, the Enrollment URL in the SCEP URL field and the API Secret in the Static Challenge and Confirm Challenge Phrase fields, so devices send their certificate requests to SecureW2.

To create a device management platform, perform the following steps:

  1. Navigate to Integration Hub > Device Management Platforms.
  2. Click Add.
  3. In the Basic section, enter the name of the device management platform in the Name field.
  4. In the Description field, enter a suitable description for the device management platform.
  5. From the Type drop-down list, select SCEP (Multi-Vendor) Enrollment Token.
  6. From the Vendor drop-down list, select Workspace ONE.
  7. From the Certificate Authority drop-down list, select the intermediate CA you created earlier in the Creating an Intermediate CA for Workspace ONE SCEP Gateway Integration section.
  8. Click Save. The following actions occur:
    1. A .csv file containing the API Secret and Enrollment URL is downloaded, and the Enrollment URL is displayed on the page.
    2. A Default Workspace ONE Certificate Template is created in the Certificate Templates section.

NOTE: Save the file securely. This file is downloaded only once during token creation. If the file is lost, the API Secret cannot be retrieved.

Configuring the Default Workspace ONE Certificate Template

A certificate template defines the attributes included in a certificate issued by a Certificate Authority (CA), the values assigned to each attribute, and the certificate’s intended use.

SecureW2 recommends using the Default Workspace ONE Certificate Template. It is generated automatically when you create a Workspace ONE SCEP token in Device Management Platforms (refer to the Creating a Device Management Platform section). You select this template later in the Enrollment Policy.

To configure the Default Workspace ONE Certificate Template, perform the following steps:

  1. Navigate to Dynamic PKI > Certificate Authorities and scroll to the Certificate Templates section.
  2. Click the Edit icon next to Default Workspace ONE Certificate Template.
  3. In the Validity Period field, enter the validity period of the certificate (based on the requirement).
  4. From the Signature Algorithm drop-down list, select the signature algorithm for the certificate signing request.
  5. In the Extended Key Usage section, from the Use Certificate For list, select Client Authentication.
  6. Click Update.

NOTE: If you have any queries related to the certificate template, contact the Support team at support@securew2.com.

Policy Management

This section explains how to set up the policies related to certificate enrollment. Through Policy Management, you can set rules for each policy to select the correct certificate template for issuing the appropriate certificate.

This section outlines the policies required in the JoinNow Management Portal to enable SCEP-based enrollment.

  1. Policy Workflow
  2. Enrollment Policy

Configuring a Policy Workflow

The Policy Workflow defines the conditions that a device must meet to be enrolled for a certificate. It uses the Device Management Platform you created for Workspace ONE as its Core Provider.

To configure a Policy Workflow, perform the following steps:

  1. Navigate to Policy Management > Policy Workflows.
  2. Click Add Policy Workflow.
  3. In the Basic section, enter the name of the policy workflow in the Name field.
  4. In the Display Description field, enter a suitable description for the policy workflow.
  5. Click Save. The page refreshes, and the Conditions tab is displayed.
  6. Select the Conditions tab.
  7. In the Conditions section, from the Core Provider drop-down list, select the device management platform that you created earlier (refer to the Creating a Device Management Platform section).
  8. Click Update.

Configuring an Enrollment Policy

The Enrollment Policy defines which certificate template and Certificate Authority are used to issue certificates to devices. It applies to the Policy Workflow you created earlier and uses the intermediate CA and certificate template you configured for Workspace ONE.

To configure an enrollment policy, perform the following steps:

  1. Navigate to Policy Management > Enrollment.
  2. Click Add Enrollment Policy.
  3. In the Basic section, enter the name of the enrollment policy in the Name field.
  4. In the Display Description field, enter a suitable description for the enrollment policy.
  5. Click Save. The page refreshes, and the Conditions and Settings tabs are displayed.
  6. Select the Conditions tab.
  7. In the Conditions section, from the Policy Workflow list, select the Policy Workflow you created earlier (refer to the Configuring a Policy Workflow section).
  8. From the Device Role list, select DEFAULT DEVICE ROLE POLICY 1.
  9. Select the Settings tab.
  10. In the Settings section, from the Use Certificate Authority drop-down list, select the intermediate CA you created earlier (refer to the Creating an Intermediate CA for Workspace One SCEP Gateway Integration section).
  11. From the Use Certificate Template drop-down list, select the Default Workspace ONE Certificate Template (refer to the Configuring the Default Workspace ONE Certificate Template section).
  12. In the other settings, the default values are retained.
  13. Click Update. 

Exporting the RADIUS Root CA

The RADIUS Root CA certificate is required to create the profile in Workspace ONE UEM. You upload it to the profile’s Credentials payload (refer to the Configuring the Credentials Payload section). This section describes how to download this certificate from the JoinNow Management Portal.

To download the RADIUS Root CA, perform the following steps:

  1. Navigate to Device Onboarding > Profiles.
  2. On the Profiles page, click the Edit link for the network profile you configured earlier.
  3. Scroll down to the Certificates section and click Add/Remove Certificate.
  4. In the Certificates dialog box, locate DigiCert Global Root G3 (Fri Jan 15 12:00:00 UTC 2038) with the type PUBLIC, and click the Download icon next to it.
  5. Click Update.

Configuring Workspace ONE UEM

This section describes how to configure Workspace ONE UEM to enroll managed devices for certificates from the JoinNow Management Portal through the SCEP protocol.

  1. Creating a Certificate Authority
  2. Creating a Certificate Template
  3. Creating a Profile

Creating a Certificate Authority

A Certificate Authority in Workspace ONE UEM defines the SCEP server from which Workspace ONE requests certificates for managed devices. Here, you add the SecureW2 SCEP server as a Certificate Authority using the Enrollment URL and API Secret from the JoinNow Management Portal.

To create a Certificate Authority, perform the following steps:

  1. Log in to the Workspace ONE UEM Portal.
  2. Navigate to Groups & Settings > All Settings > System > Enterprise Integration > Certificate Authorities.
  3. Under the Certificate Authorities tab, click + Add.
  4. In the Certificate Authority – Add/Edit dialog box:
    1. In the Name field, enter the name of the certificate authority.
    2. In the Description field, enter a suitable description for the certificate authority.
    3. From the Authority Type drop-down list, select Generic SCEP.
    4. In the SCEP URL field, enter the Enrollment URL from the downloaded .csv file (refer to the Creating a Device Management Platform section). Workspace ONE uses this URL to send certificate requests to SecureW2.
    5. In the Challenge Type field, select STATIC.
    6. In the Static Challenge and Confirm Challenge Phrase fields, enter the API Secret obtained from the downloaded .csv file (refer to the Creating a Device Management Platform section).
    7.  Retain the default values in the Retry Timeout In Milliseconds and Max Retries When Pending fields.
    8. Set the Enable Proxy toggle to DISABLED.
  5. Click SAVE.

Creating a Certificate Template

A certificate template defines the details of the certificates that Workspace ONE requests from the Certificate Authority.

To create a certificate template, perform the following steps:

  1. Navigate to Groups & Settings > All Settings > System > Enterprise Integration > Certificate Authorities.
  2. Under the Request Templates tab, click + Add.
  3. In the Certificate Template – Add/Edit dialog box:
    1. In the Name field, enter the name of the certificate template.
    2. In the Description field, enter a suitable description for the certificate template.
    3. From the Certificate Authority drop-down list, select the CA you created earlier (refer to the Creating a Certificate Authority section).
    4. Click the + button next to the Subject Name field and select CN={EnrollmentUser}.
    5. From the Private Key Length drop-down list, select 2048.
    6. In the Private Key Type field, select both Signing and Encryption.
    7. In the SAN Type section, click + Add.
      1. From the drop-down list, select Email address, and in the corresponding field, enter {DeviceSerialNumber};;{DeviceReportedName};;{EmailAddress};;;;;;{DeviceOperatingSystem};{DevicePlatform}
    8. In the Automatic Certificate Renewal field, set the toggle to ENABLED.
    9. In the Publish Private Key field, set the toggle to DISABLED.
  4. Click Save.

Creating a Profile

A profile delivers certificates and Wi-Fi settings to managed devices, enabling them to connect to the network using certificate-based authentication. In this section, you create a profile that requests a device certificate from the Certificate Authority (CA), installs the Root CA and SecureW2 Issuing CA certificates, and configures the Wi-Fi network.

This procedure creates a profile for Windows devices as an example.

To create a profile, perform the following steps:

  1. Navigate to Resources > Profiles & Baselines > Profiles.
  2. Click ADD > Add Profile.
  3. On the Add Profile page, select Windows.
  4. Select Windows Desktop > Device Profile.

Configuring the General Settings

To configure the general settings, perform the following steps: 

  1. In the General section, in the Name field, enter the name of the profile.
  2. In the Smart Groups field, select a group to assign the profile to the devices.

Configuring the Credentials Payload

The Credentials payload installs the certificates that managed devices use for certificate-based authentication on the network.

To configure the credentials payload, perform the following steps:

  1. Select the Credentials payload and click Configure.
  2. In the Credentials section (device certificate):
    1. From the Credential Source drop-down list, select Defined Certificate Authority.
    2. From the Certificate Authority drop-down list, select the CA you created earlier (refer to the Creating a Certificate Authority section). The corresponding template you created earlier (refer to the Creating a Certificate Template section) is displayed in the Certificate Template drop-down list.
    3. From the Key Location drop-down list, select TPM If Present.
    4. From the Certificate Store drop-down list, select Personal.
  3. Click the + button at the bottom right to add another credential.
  4. In the Credentials #2 section (RADIUS Root CA certificate):
    1. From the Credential Source drop-down list, select Upload.
    2. In the Add pop-up window, click Choose file and select the RADIUS Root CA certificate you want to upload.
    3. Click Save.
    4. From the Certificate Store drop-down list, select Trusted Root.

Configuring the Wi-Fi Payload

The Wi-Fi payload defines the network settings that managed devices use to connect to the Wi-Fi network with their device certificate.

To configure a Wi-Fi payload, perform the following steps:

  1. Select the Wi-Fi payload and click Configure.
  2. In the Wi-Fi section:
    1. Under the General section, in the Service Set Identifier field, enter the name of the SSID.
    2. From the Security Type drop-down list, select WPA2 Enterprise.
    3. From the Encryption drop-down list, select AES.
    4. Under the Protocols section, from the Protocols drop-down list, select Certificate.
    5. Under the Authentication section, from the Identity Certificate drop-down list, select Certificate #1 (created in the Credentials section).
    6. Under the Trust section, in the Trusted Certificates list, select Certificate #2 (the RADIUS Root CA certificate you uploaded).
  3. Click Save and Publish.

Enabling Certificate-Based Authentication with Workspace ONE and the SecureW2 SCEP Gateway

Organizations have faced challenges issuing certificates to every device on the Wi-Fi network during past events. Now, with the SecureW2 SCEP Gateway, organizations can remove pre-shared key requirements and improve authentication by following the steps in this article on configuring EAP-TLS with Workspace ONE. By creating the SCEP profile in Workspace ONE, managed devices can be enrolled for digital certificates automatically without end-users needing to do anything.

With the JoinNow Connector PKI, you can attain superior network security based on device trust and improve the user experience. By integrating SecureW2 with Workspace ONE for SCEP certificate enrollment, your organization enjoys streamlined certificate distribution at an affordable cost. For more information, click here to see our pricing details.