Key Takeaways
- PEAP-MSCHAPv2, a password-based authentication protocol, is vulnerable to credential theft due to misconfigurations and weak encryption.
- Attackers can exploit misconfigured devices by imitating legitimate networks and decrypting user credentials.
- Organizations should switch to EAP-TLS with server certificate validation to eliminate credential-based risks.
- SecureW2 JoinNow Dynamic PKI simplifies the transition to EAP-TLS, ensuring secure, certificate-based authentication.
In 2013, Microsoft released a report on a known security vulnerability in PEAP-MSCHAPv2 Wi-Fi authentication. This authentication protocol is a widely used standard, and it can be exploited to obtain user credentials from devices that are not properly configured.
Organizations can avoid this security issue by configuring devices for server certificate validation or replacing the PEAP-MSCHAPv2 protocol with Extensible Authentication Protocol–Transport Layer Security (EAP-TLS).
In this article, we’ll cover what these protocols are, the vulnerabilities behind PEAP-MSCHAPv2, and considerations for enhancing network security.
What Is MSCHAP?
MSCHAP (Microsoft Challenge-Handshake Authentication Protocol) is Microsoft’s version of the Challenge-Handshake Authentication Protocol (CHAP), a password-based method that proves a user knows a password without sending the password itself over the link. It exists in two versions: MS-CHAPv1, defined in RFC 2433, and MS-CHAPv2, defined in RFC 2759.
MSCHAPv2 is the version in common use today. Key features of MSCHAPv2 include:
- Mutual authentication: The client and server verify one another.
- Challenge response: It derives its challenge response from the NT hash of the user’s password, which is the MD4 (Message-Digest Algorithm 4) hash of that password. The plaintext password is never transmitted.
MSCHAP is most often seen as the inner authentication method inside PEAP for Wi-Fi and as a virtual private network (VPN) authentication option.
PEAP-MSCHAPv2 belongs to the family of Extensible Authentication Protocol (EAP) methods used in WPA2-Enterprise Wi-Fi.
Why MSCHAP Is Vulnerable
The MSCHAP vulnerability comes from its underlying cryptography. MSCHAPv2 uses the NT hash. This hash is an MD4 hash, and MD4 has been considered cryptographically broken for years.
In 2012, security researchers Moxie Marlinspike and David Hulton presented work at DEFCON (released as the chapcrack tool with the CloudCracker service) showing that a captured MSCHAPv2 handshake can be compromised by breaking a single DES (56-bit) key, regardless of how strong the underlying password is.
PEAP is meant to mitigate this by wrapping the MSCHAPv2 exchange inside an encrypted TLS tunnel so it cannot be read over the air.
Warning: That protection holds only if the client validates the Remote Authentication Dial-In User Service (RADIUS) server’s certificate. When a device skips server certificate validation, an attacker running an evil twin or rogue access point can terminate the TLS tunnel itself, capture the inner MSCHAPv2 handshake, and then crack it offline.
This means misconfiguration, rather than weak cryptography, is the primary issue.
See your security gap before attackers do.
See continuous trust in action on a platform that includes RADIUS, PKI and AI security.
The Security Risks of PEAP-MSCHAPv2 Device Misconfiguration
The protection PEAP offers MSCHAPv2 comes from wrapping the exchange in an encrypted TLS tunnel. But that protection depends on the client verifying that the RADIUS server has a trusted certificate.
If server certificate validation isn’t properly configured, or if it is disabled, the device could connect to a rogue network and unknowingly send its authentication exchange to an attacker.
Here’s an example scenario to consider:
- Attacker creates a rogue access point: An attacker can imitate a trusted access point from their own laptop, for instance, on a college campus.
- Device connects automatically: A student whose device has not been configured properly for the school’s legitimate SSID will connect to the nearby imitation SSID automatically and will attempt to auto-authenticate with the attacker’s spoofed network.
- Attacker captures authentication exchange: The device doesn’t verify the server’s identity, so it sends encrypted packets containing the user’s login information to the attacker’s computer.
- Attacker attempts to crack the response: A well-documented weakness in PEAP-MSCHAPv2’s encryption method allows the attacker to decrypt the packets, making it easy to acquire the user’s login credentials.
Vulnerabilities like this are exactly why industry titans like Microsoft have recommended moving away from PEAP-MSCHAPv2.
“If you're using WiFi and VPN endpoints that are based on MS-CHAPv2, they're subject to similar attacks…For WiFi and VPN connections, it's recommended to move from MSCHAPv2-based connections (such as PEAP-MSCHAPv2 and EAP-MSCHAPv2), to certificate-based authentication (such as PEAP-TLS or EAP-TLS).Microsoft
Differences Between MSCHAP and MSCHAPv2
The original MSCHAP (MS-CHAPv1) and MSCHAPv2 are both challenge-response password protocols, but MSCHAPv2 added mutual authentication and other fixes.
The table below summarizes the differences. Neither version is considered safe for modern networks without a TLS tunnel and validated server certificates.
|
Feature |
MS-CHAPv1 |
MS-CHAPv2 |
|---|---|---|
|
Defining RFC |
RFC 2433 |
RFC 2759 |
|
Authentication |
One-way (server authenticates client) |
Mutual (client also verifies server) |
|
Password handling |
NT hash (MD4); LM hash also used |
NT hash (MD4) only; plaintext never sent |
|
Known weakness |
Weak hashing; broken |
Reduces to a single DES key when handshake is captured (2012) |
RADIUS Server Certificate Validation
Microsoft provides recommendations to help users secure their devices, and a vital part of the defense relies on server certificate validation.
Info: Server certificate validation is a security check that allows a device to verify a RADIUS server’s identity before it exchanges authentication information with that server.
During PEAP-MSCHAPv2 authentication, the RADIUS server presents a digital certificate to the connecting device, and the device checks a few things:
- Whether the certificate was issued by a trusted certificate authority (CA) — this can be a public CA or an internal CA managed by an IT department.
- Whether the certificate is valid.
- Whether the RADIUS server is an authorized server.
Server certificate validation prevents over-the-air credential theft by verifying that the RADIUS server possesses the trusted certificate. This confirms that the network is legitimate and will allow the device to connect.
Warning: Failure to verify the server certificate leaves users and devices susceptible to Active Directory or LDAP credential theft via a simple man-in-the-middle attack.
Watch the video below for a deeper look at MS-CHAPv2 and its security vulnerabilities from security researcher Vivek Ramachandran.
Enforce Server Certificate Validation on Every Device
Server certificate validation should be enabled on every device that connects to a network using PEAP-MSCHAPv2. That means configuring each device to trust the right CA, verify the server certificate, and connect only to approved authentication servers.
Configuration varies across operating systems and devices, so organizations with large bring-your-own-device (BYOD) environments face greater challenges because they have less control over how employees and students configure personal devices.
Relying on individuals to configure their device settings manually can lead to:
- Skipped security settings: Users might overlook server certificate validation or leave it disabled.
- Incorrect certificate trust: Users may receive an untrusted certificate prompt to complete their connection, allowing a rogue server to impersonate your network.
- Inconsistent configurations: You have less control over configurations across different devices, as they use different certificate authorities or server settings.
- Increased IT workload: When users connect their own devices to a network, it can lead to more troubleshooting for your IT team as they process certificate errors and authentication failures.
Auto-configuration tools can help mitigate these concerns and create consistency across your network.
The security plan that scales with you.
Our solutions can scale from mid-market to global enterprises. Compare options and see how our solutions protect you from costly breaches and ensure peace of mind.
EAP-TLS Factors Device Trust Into Network Security
So, with PEAP-MSCHAPv2’s vulnerabilities, what is the alternative? The answer is EAP-TLS authentication. This protocol allows organizations to replace credentials with certificates for enhanced, passwordless network security.
With EAP-TLS, you get:
- Lower risk: The risk of over-the-air credential theft is null because no credentials are sent over the air.
- Encrypted tunnel: Certificates are sent through the encrypted EAP tunnel and cannot be intercepted by a MITM attack.
- Identity binding: Certificates are tied to the identity of the user and device and cannot be stolen or removed from the device.
- Device trust: You can factor in device trust, allowing only trusted managed devices that you know have up-to-date security policies enforced on the network.
EAP-TLS also provides a far superior end-user experience, primarily by eliminating the burdens associated with using passwords. You can eliminate password change policies that reset all network devices and require users to reconnect their many devices. What’s more, users won’t need to come up with new and complex passwords for every single resource they need to log into.
In contrast, certificates are preset to expire after a chosen interval. This timeframe can be as long or short as the organization desires. Devices equipped with certificates also authenticate and connect to the network faster because there are significantly fewer steps to authenticate a certificate compared to credentials.
Moving to certificate-based 802.1X authentication removes the MSCHAP attack surface entirely, because there is no password hash for an attacker to capture or crack.
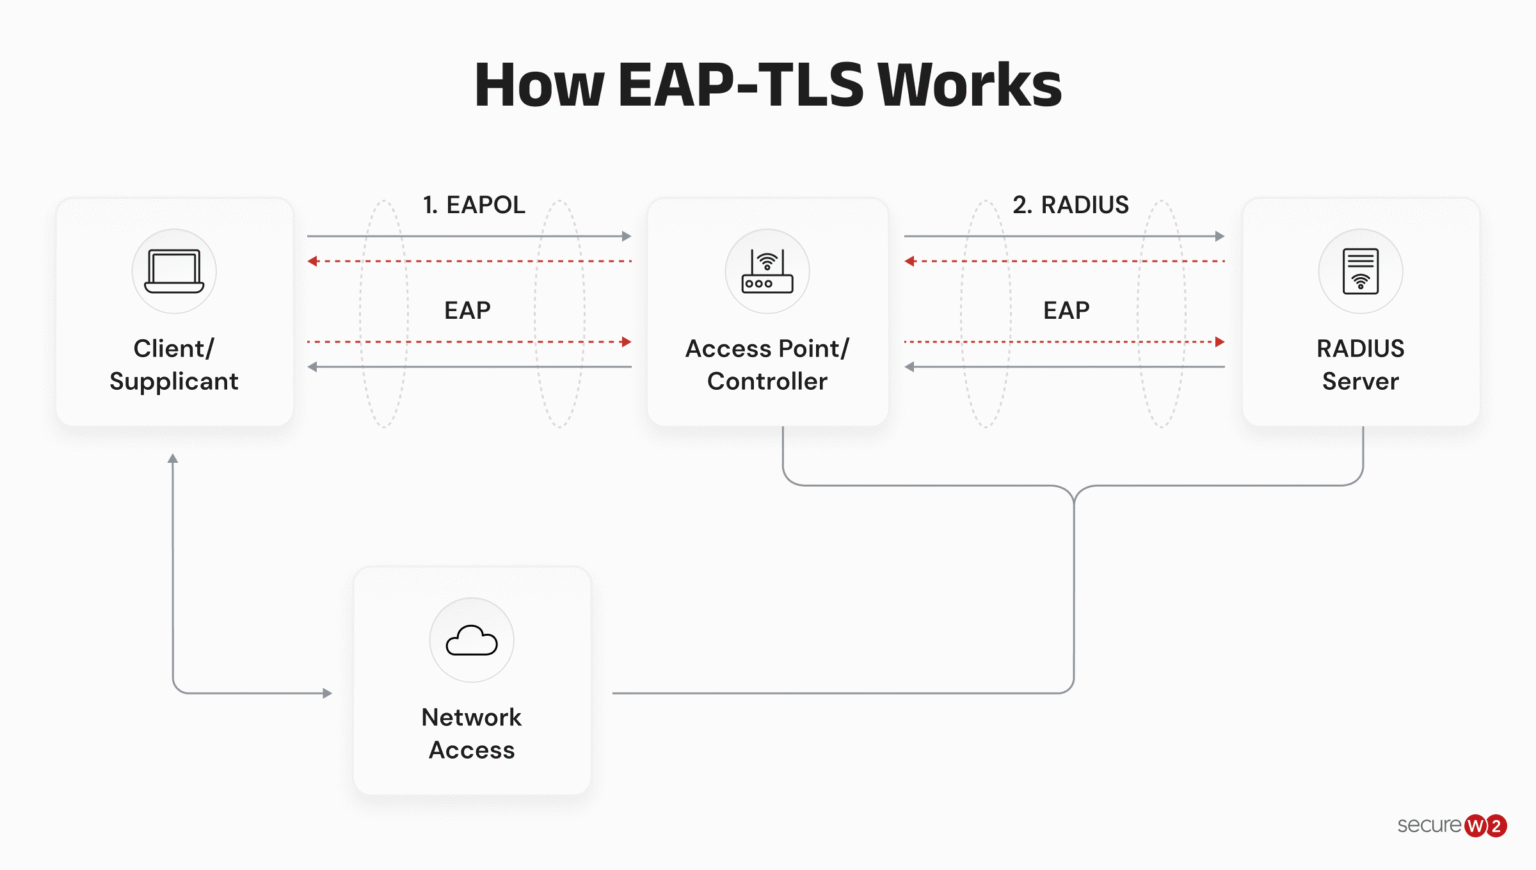
The image below shows how EAP-TLS works between a client device, an access point, and a RADIUS server. For more information, read our complete guide: EAP-TLS Explained: How It Works and Why It’s Secure.
EAP-TLS 1.3 Delivers the Best Security
PEAP-MSCHAPv2 has been widely used for enterprise Wi-Fi authentication, but it lacks several security features that modern organizations expect.
IETF RFC 9190, published in 2022, defines EAP-TLS with TLS 1.3 and introduces stronger protections that password-based authentication methods cannot provide.
EAP-TLS 1.3 provides forward secrecy, protects the client’s identity during authentication and requires certificate revocation checking. These features improve both security and privacy for enterprise wireless networks.
Forward Secrecy Protects Past Sessions
Forward secrecy means that every authentication session uses unique encryption keys. Even if a certificate is compromised in the future, previously captured network traffic cannot be decrypted.
PEAP-MSCHAPv2 does not provide this protection because authentication depends on the user’s password. If that password is later compromised, attackers may use it to target past or future authentication attempts.
Identity Privacy Protects User Information
EAP-TLS 1.3 keeps the client’s identity protected inside the encrypted TLS tunnel. This makes it more difficult for attackers to collect user information by monitoring network traffic.
In contrast, PEAP-MSCHAPv2 relies on password-based authentication and does not offer the same level of identity protection.
Certificate Revocation Limits Unauthorized Access
If a device is lost or compromised, its certificate can be revoked, preventing it from authenticating to the network. PEAP-MSCHAPv2 does not use client certificates, so there is no equivalent way to revoke access without changing user credentials.
Certificate-based Authentication Supports Future Cryptographic Changes
EAP-TLS is better positioned for future cryptographic changes. As organizations prepare for post-quantum cryptography, certificate-based authentication can adopt new algorithms by updating the public key infrastructure (PKI). PEAP-MSCHAPv2 relies on passwords rather than certificates, so it cannot use the same migration path.
For organizations planning their long-term authentication strategy, EAP-TLS 1.3 provides stronger security, better privacy and greater flexibility than PEAP-MSCHAPv2.
EAP-TLS 1.3 addresses today’s enterprise security requirements and provides a foundation that can evolve as authentication standards continue to advance.
Replacing PEAP-MSCHAPv2 With EAP-TLS Is Simple With SecureW2
Continuing to use credentials is a huge risk; all it takes is one stolen credential for a hacker to slip into your network. The majority of people reuse passwords, so capturing one set of credentials can be like snatching a master key that bad actors can use to access additional resources and wreak havoc across an organization.
This is why an increasing number of organizations are moving to certificate-based authentication.
Some organizations opt to ease the transition to certificate authentication by implementing the simultaneous support that SecureW2 provides for PEAP and EAP-TLS. This top university chose to enroll all incoming students for certificate-based authentication while phasing out credentials in stages with existing users.
The JoinNow Platform can configure security essentials, such as server certificate validation, on a wide range of BYOD platforms (Windows, Mac, iOS, Android, Linux, Kindle, and more). Rather than going through a risky and difficult process of manually configuring their personal devices, users can rest assured that they are onboarding in the easiest and most secure manner possible.
The JoinNow Platform also incorporates JoinNow Dynamic PKI, which allows organizations to easily deploy EAP-TLS certificate-based authentication on their campus.
SecureW2 provides affordable options to protect against credential theft. Schedule a demo to see how quickly you can retire MSCHAP and move to certificate-based authentication with JoinNow Cloud RADIUS.
Frequently Asked Questions
What does MSCHAP stand for?
MSCHAP stands for Microsoft Challenge-Handshake Authentication Protocol. It is Microsoft’s version of CHAP, a password-based authentication protocol. The current version, MSCHAPv2, is defined in RFC 2759 and is most commonly used as the inner authentication method inside PEAP for Wi-Fi and as a VPN authentication option.
Is MSCHAPv2 secure?
On its own, no. A captured MSCHAPv2 handshake can be reduced to breaking a single DES key, which dedicated hardware can recover in under a day regardless of password strength. PEAP wraps MSCHAPv2 in a TLS tunnel for over-the-air protection, but that protection fails if the client does not validate the RADIUS server certificate. For long-term security, certificate-based EAP-TLS is the recommended replacement.
What is the difference between MSCHAP and MSCHAPv2?
MSCHAP (MS-CHAPv1, RFC 2433) provides one-way authentication, where the server authenticates the client. MSCHAPv2 (RFC 2759) adds mutual authentication so the client also verifies the server, and it drops the weaker LM hash in favor of the NT hash. Both still rely on the MD4-based NT hash and are vulnerable when a handshake is captured, so neither is safe without a validated TLS tunnel.
How to replace PEAP-MSCHAPv2 authentication?
The recommended alternative is EAP-TLS, a certificate-based 802.1X authentication method. Instead of a password and its hash, each device presents a digital certificate that cannot be intercepted over the air or reused on another device. Because no password hash crosses the network, the MSCHAP cracking attack does not apply. Microsoft has recommended moving to certificate-based authentication such as EAP-TLS for MSCHAPv2-based Wi-Fi and VPN endpoints.
