Key Takeaways
- AAA servers handle authentication, authorization, and accounting for secure network access control.
- AAA servers support more secure certificate-based authentication using EAP-TLS, reducing risks and improving user experience.
- SecureW2 JoinNow Cloud RADIUS offers a robust, dynamic AAA solution for secure, policy-driven authentication and seamless network management.
AAA servers are the backbone of network access control. Every time a user connects to a Wi-Fi network, authenticates to a virtual private network (VPN), or logs in to a managed device, an AAA server is usually making the decision behind the scenes, asking questions like:
- Is this person who they claim to be?
- What should they be allowed to access?
- What did they do once connected?
This guide breaks down how AAA servers work, the protocols they use, and how modern organizations deploy them to secure network access at scale.
Watch a SecureW2 expert explain the role of AAA servers in network security:
What Is an AAA Server and What Does AAA Stand For?
An AAA server is a centralized security system that verifies user identities, controls access to network resources, enforces security policies, and tracks network activity. AAA stands for authentication, authorization, and accounting.
These three functions form a framework that governs how users and devices gain access to network resources, what they can do once connected, and how their activity gets logged.
“Authentication is the act of deciding whether someone should be let on the network. That process entails receiving the request when someone clicks on the Wi-Fi, validating the source of truth, and then telling the network infrastructure this person should be let in.”
Micah Spady, Director of Product Marketing at SecureW2
- Authentication verifies identity. A user or device presents credentials (a password, a certificate, a token), and the AAA server checks those credentials against an identity store.
- Authorization determines permissions. After authentication, the server applies policies that define which resources, VLANs, or services the user can access.
- Accounting records activity. The server logs session details such as connection time, data usage, and which resources were accessed, creating an audit trail for compliance and troubleshooting.
These three processes can run together or separately, depending on the protocol. Remote Authentication Dial-In User Service (RADIUS) combines authentication and authorization into a single step. Terminal Access Controller Access-Control System Plus (TACACS+) separates all three, giving administrators more granular control.
Where Are AAA Servers Used?
Organizations deploy AAA servers wherever they need centralized access control. Common use cases include:
- Enterprise Wi-Fi (802.1X): AAA servers authenticate users and devices connecting to WPA2-Enterprise or WPA3 wireless networks.
- VPN authentication: Remote workers connect through a VPN gateway that checks credentials against an AAA server before granting tunnel access.
- Network device administration: Routers, switches, and firewalls use AAA to control which administrators can log in and which commands they can execute.
- Guest and bring-your-own-device (BYOD) access: Organizations use AAA to segment guest users onto restricted VLANs while giving managed devices full network access.
- Internet service provider (ISP) and carrier networks: ISPs use AAA for subscriber authentication, bandwidth tracking, and usage-based billing.
Any organization with more than a handful of network users benefits from centralized AAA. Without it, every access point, switch, and VPN gateway would need its own local user database, which is a maintenance and security liability.
See your security gap before attackers do.
See continuous trust in action on a platform that includes RADIUS, PKI and AI security.
Why Do You Need an AAA Server?
An AAA server helps secure network access by verifying individual user and device identities, enforcing access policies, and tracking network activity. Unlike a shared password, it gives administrators control over who can connect, what they can access, and how their activity is recorded.
Pre-shared keys (PSKs) are the simplest form of wireless security, but they become difficult to manage at scale. A single password shared across every user and device means:
- No way to identify individual users on the network
- No way to revoke access for a single person without changing the key for everyone
- No audit trail linking sessions to specific identities
- No ability to enforce role-based access policies
AAA servers solve all of these problems by authenticating each user or device individually, applying policies to determine what each identity can access, and logging session details to support compliance and troubleshooting.
Credential theft and misuse are major contributors to data breaches. Moving from shared passwords to per-user or per-device authentication, especially certificate-based authentication, removes the most common attack vector from the network edge.
To see how AAA works in practice, it helps to understand RADIUS, a protocol that handles authentication and authorization for network access. Watch the video below for an overview.
How Does an AAA Server Work?
An AAA server sits between the user’s device and the network resources they want to access. Here is the step-by-step flow for a typical 802.1X wireless authentication:
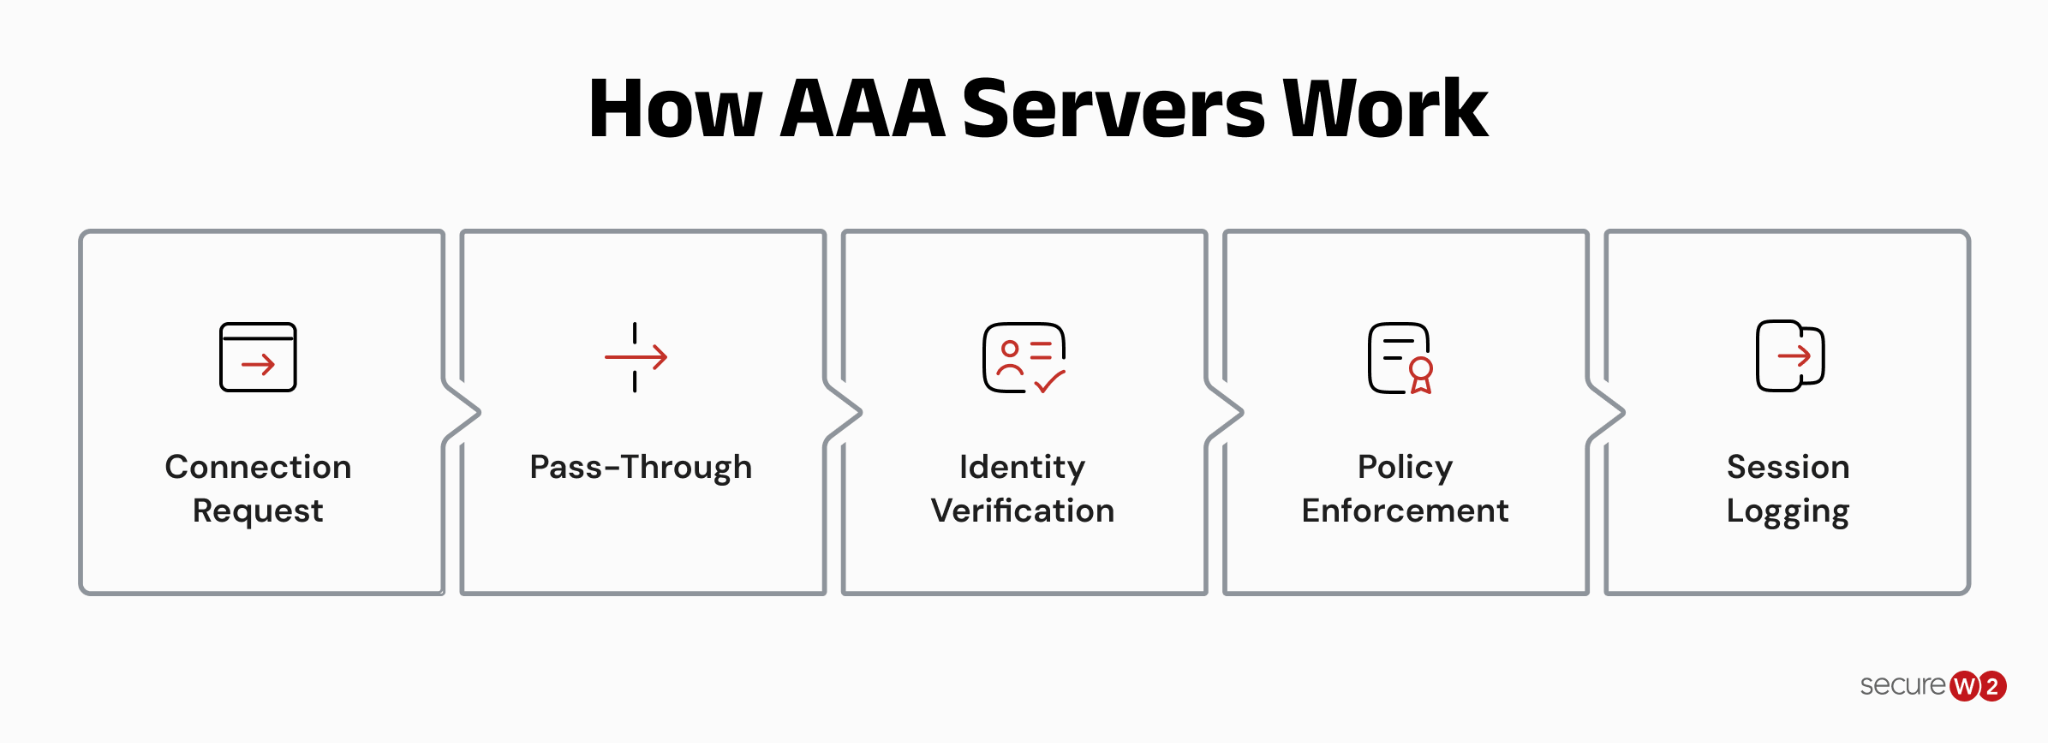
1. Connection Request (Supplicant)
The user’s device (the supplicant) associates with a wireless access point or plugs into a wired switch port. The network enforces 802.1X, which means no traffic passes until the device authenticates.
2. Pass-Through (Authenticator)
The access point or switch acts as an intermediary. It does not make access decisions. Instead, it packages the user’s credentials into a RADIUS Access-Request and forwards them to the AAA server.
3. Identity Verification (Authentication)
The AAA server receives the request and checks the credentials against an identity provider. This could be a cloud directory like Entra ID or Okta, an on-premises Active Directory, or an LDAP store.
The server supports authentication protocols such as:
- EAP-TLS: Under this certificate-based authentication protocol, the server and client exchange X.509 digital certificates; no passwords are used.
- PEAP-MSCHAPv2: The server presents a certificate to create an encrypted tunnel, then the client sends a username and password inside it.
- EAP-TTLS/PAP: This protocol is similar to PEAP but offers broader client support; it is still password-based.
If credentials are valid, the server sends an Access-Accept. If not, Access-Reject.
4. Policy Enforcement (Authorization)
On a successful authentication, the AAA server can send authorization attributes back to the access point. These attributes tell the network how to treat the session:
- Assign the device to a specific virtual local area network (VLAN).
- Apply bandwidth limits or quality of service (QoS) policies.
- Grant or restrict access to specific subnets.
- Enforce session timeouts or re-authentication intervals.
This is where policy-driven access control happens. An employee device with a valid certificate and a compliant posture might land on the corporate VLAN. A personal BYOD device might get a restricted VLAN with internet-only access.
5. Session Logging (Accounting)
Once the session is active, the AAA server records accounting data:
- User’s identity
- MAC address of the device
- Assigned VLAN
- Session start and end times
- Data transferred
These records feed into SIEM platforms, compliance reports, and capacity planning tools.
AAA Protocols: RADIUS vs. TACACS+ vs. Diameter
Three protocols handle AAA communication between network devices and servers. Each has a different architecture and use case. The table below compares the three protocols:
|
Feature |
RADIUS |
TACACS+ |
Diameter |
|---|---|---|---|
|
Primary use |
Network access |
Network device administration |
Mobile and carrier networks |
|
Transport |
UDP (ports 1812/1813) |
TCP (port 49) |
TCP or SCTP |
|
Encryption |
Encrypts only the password field in Access-Request packets |
Encrypts the entire packet payload, not just the password |
Supports TLS/DTLS natively |
|
AAA model |
Combines authentication and authorization |
Separates authentication, authorization, and accounting |
Supports separate, extensible AAA functions |
|
Common applications |
Wi-Fi, VPNs, 802.1X |
Router, switch, and firewall administration |
LTE, 5G, and carrier services |
The encryption row describes the protocols' standard behavior; implementations and security extensions can change how traffic is protected.
RADIUS (Remote Authentication Dial-In User Service)
RADIUS is the dominant AAA protocol for network access. Nearly every wireless access point, VPN gateway, and network switch supports it.
RADIUS is defined in RFC 2865 and has been extended many times. Its simplicity and universal vendor support make it the default choice for network access control.
One limitation: RADIUS uses UDP, which means there is no built-in retransmission if a packet is lost. Modern implementations handle this at the application layer, and RadSec (RADIUS over TLS) adds encryption and TCP reliability for deployments that need it.
TACACS+ (Terminal Access Controller Access-Control System Plus)
TACACS+ is designed for device administration rather than network access.
TACACS+ gives network teams fine-grained control over who can run which commands on which devices. A junior network engineer might be authorized to view configurations but not modify them, while a senior engineer gets full access.
The trade-off is vendor support. TACACS+ originated at Cisco and has the deepest support in Cisco environments. Multi-vendor networks typically use RADIUS for user access and TACACS+ for device administration.
Diameter
Diameter is the successor to RADIUS, designed for mobile and carrier networks.
Most enterprise IT teams will not interact with Diameter directly. It lives in the telecom infrastructure layer. But if your organization operates a mobile network or provides carrier-grade services, Diameter is the protocol handling subscriber AAA.
Watch the video below to learn why RADIUS is important for 802.1X authentication:
Credential-Based vs. Certificate-Based AAA Authentication
How you authenticate matters as much as whether you authenticate. The two main approaches to authentication differ significantly in security and operational overhead.
Password-Based Authentication
Most AAA deployments start with passwords. Users type a username and password, and the AAA server checks them against a directory. Protocols like PEAP-MSCHAPv2 protect the exchange inside an encrypted tunnel, but the underlying credentials are still vulnerable to:
- Phishing: Users can be tricked into entering credentials on fake captive portals or spoofed login pages.
- Over-the-air attacks: PEAP-MSCHAPv2 credentials can be intercepted and cracked if the client does not properly validate the server certificate.
- Password reuse: Users who recycle passwords across services expose the network to credential stuffing.
- Helpdesk load: Password resets, expiration policies, and lockouts generate a constant stream of support tickets.
Certificate-Based Authentication (EAP-TLS)
Certificate-based authentication replaces passwords with X.509 digital certificates. Each user or device receives a certificate from a trusted certificate authority (CA). During authentication, the supplicant and the AAA server exchange certificates and prove identity through public-key cryptography.
This approach eliminates the password attack surface entirely:
- Certificates cannot be phished (there is nothing for the user to type).
- The private key never leaves the device and cannot be extracted.
- There are no passwords to reset, expire, or share.
- EAP-TLS is the strongest authentication protocol available for 802.1X.
The traditional barrier to certificate-based authentication has been the complexity of running a public key infrastructure (PKI). Issuing, renewing, and revoking certificates across thousands of devices used to require dedicated on-premises CA servers and specialized expertise.
Cloud-native PKI platforms have removed that barrier.
SecureW2 JoinNow Dynamic PKI automates certificate issuance through ACME Device Attestation and Dynamic SCEP, integrates with identity providers like Entra ID and Okta for identity-driven enrollment, and handles the full certificate lifecycle without on-premises infrastructure.
Benefits of Deploying an AAA Server
Deploying an AAA server improves network security by centralizing access control, enforcing user-specific permissions, and tracking network activity. Key benefits include:
- Per-user accountability: Every session ties back to an individual identity, not a shared key. This makes incident investigation, compliance reporting, and forensic analysis straightforward.
- Role-based access control: Authorization policies can segment users by department, device type, compliance status, or any attribute available in the identity provider. Finance gets access to financial systems; contractors get internet only.
- Centralized policy management: One AAA server (or cluster) controls access for every access point, switch, and VPN gateway on the network. Policy changes propagate instantly rather than requiring manual updates on each device.
- Scalability: Adding new access points or office locations does not require replicating local user databases. Every device points to the same AAA infrastructure.
- Compliance and audit readiness: Accounting logs provide the session-level detail that auditors require for frameworks like HIPAA, PCI DSS, SOC 2, and FERPA.
BlastRADIUS Changes AAA Server Security
AAA servers have relied on RADIUS for network authentication for many years. In 2024, the discovery of the BlastRADIUS vulnerability showed that one part of the protocol needed stronger protection.
As a result, organizations using RADIUS-based AAA servers should review their infrastructure to ensure it meets the latest security guidance.
What Is the BlastRADIUS Vulnerability?
The BlastRADIUS vulnerability (CVE-2024-3596) allows an attacker positioned on the network to forge a RADIUS Access-Accept message under specific conditions. This is possible because the original RADIUS specification made the Message-Authenticator attribute optional in some authentication messages.
To address this issue, the Internet Engineering Task Force (IETF) published the Deprecating Insecure Practices in RADIUS draft, which requires the Message-Authenticator attribute to be included in all Access-Request, Access-Accept, Access-Reject, Access-Challenge and Protocol-Error packets.
How Does BlastRADIUS Affect Network Access?
For IT teams, this means every part of the RADIUS environment should be updated together.
A patched AAA server may reject authentication requests from older access points, VPN gateways or network switches that do not include the required Message-Authenticator attribute. Users may simply see a failed login, even though their credentials and network policies are correct.
How Can Organizations Improve RADIUS Security?
The updated guidance also points to a longer-term change. The IETF recommends moving away from traditional RADIUS over UDP and adopting RadSec, which runs RADIUS over TLS. Encrypting RADIUS traffic provides stronger protection for authentication messages, especially when they travel across untrusted or shared networks.
Organizations reviewing their AAA infrastructure should treat the Message-Authenticator requirement as an immediate priority.
At the same time, organizations should begin planning for a future where RadSec becomes the preferred way to secure communication between RADIUS clients and AAA servers.
Keeping network devices, RADIUS servers and authentication policies up to date will improve both security and compatibility as vendors continue adopting the latest standards.
How AAA Fits Into Modern Network Security
AAA does not operate in isolation. It is one layer in a broader access control architecture that includes identity providers, device management, and security posture assessment.
AAA and Identity Providers
Modern AAA servers query cloud identity providers (Entra ID, Okta, Google Workspace) in real time during authentication. This means a disabled user account or a changed group membership takes effect on the next network connection attempt, not after a manual sync.
SecureW2 JoinNow Cloud RADIUS performs real-time identity lookups against cloud directories on every authentication. If a user is terminated in Okta at 2 p.m., their network access is revoked the next time their device re-authenticates, without any manual intervention.
AAA and Device Management
AAA servers can incorporate device posture into authorization decisions:
- Is the device managed by a mobile device management (MDM) platform such as Intune or Jamf?
- Is the endpoint agent running?
- Is the OS patched to the required version?
These signals feed into the authorization policy, determining whether a device gets full access, restricted access, or no access at all.
AAA and Network Segmentation
Authorization attributes from the AAA server drive dynamic VLAN assignment and network segmentation. Rather than statically assigning ports to VLANs, the network adapts to the identity and posture of whatever device connects. This is the practical implementation of least-privilege network access.
How to Choose the Right AAA Server for Your Network
The right AAA solution depends on your network’s scale, identity infrastructure, and security requirements. Key factors include:
- Cloud vs. on-premises: On-premises RADIUS servers (like Microsoft NPS or FreeRADIUS) require dedicated hardware, patching, and high-availability configuration. Cloud RADIUS eliminates that overhead and provides built-in redundancy.
- Identity provider integration: Your AAA server needs real-time connectivity to your identity provider. If your directory is in the cloud (Entra ID, Okta), a cloud-native AAA server avoids the latency and failure modes of bridging cloud identity to on-premises RADIUS.
- Certificate support: If you plan to move to certificate-based authentication, choose an AAA platform that includes or integrates with a PKI for automated certificate lifecycle management.
- Vendor neutrality: Enterprise networks run hardware from multiple vendors. Your AAA server should work with any access point, switch, or VPN gateway without requiring a specific vendor ecosystem.
Ultimately, the best AAA server is one that fits your existing infrastructure while providing reliable authentication, centralized access control, and room to adapt as your network evolves.
The security plan that scales with you.
Our solutions can scale from mid-market to global enterprises. Compare options and see how our solutions protect you from costly breaches and ensure peace of mind.
Case Study: How a Restaurant Group Scaled AAA Security Across 800+ Locations
A large restaurant group needed a more secure way to manage network access across hundreds of locations. Its reliance on pre-shared keys limited visibility into individual devices and made access management more challenging.
A compliance review also uncovered more than 16,000 rogue certificates associated with payment terminals, highlighting the need for stronger authentication controls.
The organization adopted SecureW2 Cloud RADIUS and Dynamic PKI solutions to transition from shared passwords to certificate-based authentication using EAP-TLS. Over four years, the deployment expanded from 4,000 to more than 22,000 devices across 800+ locations.
Read the full case study to learn more about the organization's transition to certificate-based network authentication.
Modernize Your AAA Infrastructure With JoinNow Cloud RADIUS
A modern AAA solution should do more than authenticate users. It should connect network access decisions to real-time identity data, enforce policies across users and devices, and simplify certificate management without adding on-premises infrastructure.
SecureW2 combines Cloud RADIUS with Dynamic PKI to bring these capabilities together. Cloud RADIUS validates identities against providers like Entra ID, Okta, and Google Workspace, while Dynamic PKI automates certificate issuance and renewal for managed and BYOD devices. Together, they support scalable, certificate-based authentication across diverse network environments.
See how SecureW2 can help you strengthen network access security and simplify AAA management. Schedule a demo to explore the platform.
Frequently Asked Questions
What is the difference between RADIUS and TACACS+?
RADIUS is designed for network access control (Wi-Fi, VPN, wired 802.1X) and combines authentication and authorization into one step. TACACS+ is designed for device administration (router and switch login) and separates authentication, authorization, and accounting into independent processes. TACACS+ encrypts the full packet; RADIUS encrypts only the password. Most organizations use both: RADIUS for user network access and TACACS+ for IT staff managing network equipment.
Can an AAA server work with cloud identity providers?
Yes. Modern AAA servers integrate with cloud identity providers like Entra ID (Azure AD), Okta, and Google Workspace. The AAA server queries the identity provider during authentication to verify credentials and pull group membership or attribute data for authorization decisions. Cloud RADIUS solutions like SecureW2 perform these lookups in real time on every authentication event.
What is 802.1X and how does it relate to AAA?
802.1X is an IEEE standard for port-based network access control. It defines the communication between a device (supplicant), a network switch or access point (authenticator), and an AAA server (authentication server). 802.1X is the mechanism that enforces AAA on wired and wireless networks. Without an AAA server, 802.1X has nothing to authenticate against.
Is an AAA server the same as a RADIUS server?
Not exactly. RADIUS is one protocol that AAA servers use, but it is the most common one for network access. An AAA server running RADIUS handles the authentication, authorization, and accounting functions using the RADIUS protocol. TACACS+ and Diameter are alternative AAA protocols for different use cases. In practice, when network engineers say "AAA server" in the context of Wi-Fi or VPN, they almost always mean a RADIUS server.
How do I migrate from password-based to certificate-based AAA?
The migration typically involves three steps: deploy a PKI to issue certificates, configure your AAA server to support EAP-TLS, and enroll devices. Cloud PKI platforms simplify this by automating certificate issuance through MDM integrations (Intune, Jamf, Google Workspace) for managed devices and self-service onboarding portals for BYOD. During the transition period, the AAA server can support both password-based and certificate-based protocols simultaneously.
